The complete investigation file
Subject: Quake3, moderator of XSS.is (ex DaMaGeLaB)
Also known as: morgot (exploit.in), Rcode (per DEF CON 33)
Claim: Subject is the "Morgot / Rcode / Quake3" persona placed by DEF CON 33 reporting at the head of REvil's source-code development, the only developer of the REvil ransomware core.
Base identity (moderate confidence): Anatoly Sergeevitsch Kravchuk, born 13.06.1982 in Makiivka (Makeevka), Ukraine, the developer the German BKA named publicly in April 2026.
Method: Every claim below is anchored to dated, verbatim messages written by the subject himself, private correspondence, public posts, moderator actions. Where a claim rests on inference rather than his own words, it is labeled as such. No database identifiers are cited; what is shown is what a reader would see with the message open in front of them.
0. EXECUTIVE SUMMARY
One man ran three forum accounts on the same two IP addresses, at the same hours, for three months. One of those accounts is the forum's moderator. In private correspondence he confirmed, in his own typing, that he is morgot of exploit.in. He gave his jabber handle as [email protected] more than ten times across six years. The moderator and the persona morgot are the same person, and morgot / Rcode / Quake3 is the persona table DEF CON 33 published for REvil's source-code developer.
The man behind the accounts wrote his own biography into the record across a decade: medical education, coding from age 20+, family, real-life work, a prison sentence of two and a half years, an offline smartphone smuggled for PDFs, and a public fear, confirmed by the man who was his closest friend, that the police came asking about a woman.
This file is that biography, in his own words, in order.
1. THREE ACCOUNTS. ONE MAN.
The primary account registered on 2010-11-03 and carried a single identity for eight years. In late September and early October 2018, the same weeks the account came back from a long silence, two fresh accounts appeared. Fresh names. Fresh mailboxes. Same hands.
1.1 The account table
| Field | Quake3 | chromium | evilcore |
|---|---|---|---|
| [email protected] | [email protected] | [email protected] | |
| custom title | «генератор Зла» | , | , |
| registered | 2010-11-03 | 2018-09-29 | 2018-10-03 |
| last activity | 2018-12-11 21:21 | 2018-12-07 | 2018-12-07 |
| posts | 456 | 20 | 10 |
| timezone | Europe/Kaliningrad | Atlantic/Cape_Verde | Atlantic/Cape_Verde |
Read the password dates, each account's password was changed within four days of the others:
Quake3, password changed 2018-10-21chromium, password changed 2018-10-23evilcore, password changed 2018-10-25
Three accounts, three mailboxes, and all three keys rotated inside five days. That is not three people syncing calendars. That is one person changing his locks on a rhythm only he kept.
1.2 The IP interleaving
The three accounts shared two IP addresses. No other account on the forum used either of them.
46.200.195.40    , mobile range, used as the primary line
185.107.80.179   , secondary line, used intermittently from mid-November
The interleaving is not "shared office Wi-Fi." It is one operator flipping between masks in real time, on the same day, sometimes within the same hour:
2018-11-13
- 10:23,
Quake3on46.200.195.40 - 11:26,
chromiumon46.200.195.40(login) - 15:33–15:57,
chromiumwrites to a user about the logo contest, on46.200.195.40 - 21:59,
Quake3on46.200.195.40
2018-11-15
- 03:11,
chromiumon185.107.80.179 - 03:18,
evilcoreon185.107.80.179, resetting its own password - 16:18,
Quake3on185.107.80.179 - 21:03,
Quake3on46.200.195.40 - 21:38,
evilcoreon46.200.195.40(login) - 21:43,
evilcoreon46.200.195.40(avatar update, preferences edit) - 21:45,
evilcoreon46.200.195.40(second avatar update)
2018-11-16
- 06:25,
Quake3on46.200.195.40 - 17:54,
evilcoreon46.200.195.40 - 15:46,
Quake3on46.200.195.40
2018-11-17
- 03:44,
Quake3on46.200.195.40(edits a post) - 03:45,
Quake3on46.200.195.40(edit recorded) - 19:09,
chromiumon46.200.195.40(login)
2018-11-18, the night of the logo-contest finale
- 16:44,
Quake3on46.200.195.40 - 16:48,
Quake3on46.200.195.40(moderator edit, contest thread) - 16:49,
evilcoreon46.200.195.40(login) - 16:51,
evilcoreon46.200.195.40(edit recorded) - 17:23,
evilcorewrites in private about vote counts - 17:59,
evilcorewrites again about vote counts
Three accounts, one address, one night, forty minutes apart. Then:
2018-11-23
- 22:27,
evilcoreon185.107.80.179 - 22:41,
evilcoreon46.200.195.40, fourteen minutes later.
2018-11-27
- 15:41,
evilcoreon46.200.195.40(login) - 15:42,
Quake3deletes a thread - 15:44,
Quake3spam-cleans a user account
The accounts never overlap in a way that requires two humans. They alternate. One person logs out of one, logs into another.
2. THE HINGE: «есть. morgot»
The identity link was confirmed by the subject himself, in a private message dated 2018-10-22.
Context, from the message thread: a new moderator of the PHP/JavaScript section introduces himself to Quake3, asks for advice, and the conversation turns to background.
Quake3: Главное, удалять мусор, переносить оффтоп в общение, комерц в комерц разделы. Чтобы раздел был именно по своей тематике, а не помойка. (The main thing is to delete garbage, move off-topic to general chat, commercial stuff to commercial sections. The section should be on-topic, not a dump.)new moderator: Понял, спасибо большое за советы. Да, есть, ник тот же. (Got it, thanks a lot for the advice. Yes, I'm there, same handle.)
new moderator: А ты есть на экспе? (Are you on exploit?)
Quake3: есть. morgot (Yes. morgot.)
There it is. In his own typing: the moderator of this forum is morgot of exploit.in. He offered it casually, the way a man offers a name he assumes everyone already knows.
2.1 The jabber handle, six years of it
He gave [email protected] as his contact address over and over, across the full life of the account:
| Date | Context | Message (verbatim) |
|---|---|---|
| 2012-08-16 | web job | «Стукни мне [email protected], надо обсудить детали» |
| 2012-10-07 | SpyEye question | «ок, я бываю в инете ближе к вечеру, jid: [email protected]» |
| 2013-05-16 | MBR locker sale | «[email protected], там обсудим подробней» |
| 2013-05-19 | bot coding | «добавь меня [email protected], как состыкуемся в онлайне, обсудим» |
| 2013-08-21 | exploit.in edit | «[email protected]. Но я могу редактировать посты лишь в кодинге/веб кодинге» |
| 2013-09-05 | contact | «[email protected]» |
| 2013-11-01 | contact | «Еще есть [email protected] или как то так, но там нет пгп, есть отр» |
| 2018-11-02 | software review | «Напишите мне в жабу, я буду там ближе к вечеру. [email protected]» |
| 2018-11-09 | software review | «[email protected]» |
And the self-description, in English, dated 2018-09-29:
Quake3: me morgot on exploit.in (moderator of web-coding section) and on this one
That message is the hinge of the entire case, written in his own hand, three weeks before he gave the same answer to the same question in a private message.
2.2 The moderator's own account of his powers
Dated 2018-09-29, the subject describes his role to another user:
Quake3: Я модератор на форуме, могу редактировать/удалять любой пост на форуме, и любую тему. Еще у меня в модерке есть пункт "жалобы" и премодерация. Так же туда, как я понял, должны попадать посты не прошедшие премодерацию. Вот собственно и все, что я знаю о своих полномочиях. (I'm a moderator on the forum, I can edit/delete any post and any thread. I also have the "complaints" section and pre-moderation in the mod panel.)
Same date, a parallel message to a third party, in English: "me morgot on exploit.in (moderator of web-coding section) and on this one." Two messages, same day, two audiences, the exact same content. He was wearing both hats openly, and believed nobody would mind.
3. THE MAN THE ADMIN CALLED «КВАКА»
The subject's closest contact on the forum was the administrator himself. Their correspondence is the emotional core of the record, and it contains the IRL details that make this more than a username exercise.
3.1 The reconnect, 2018-09-25
After years of silence, the administrator reaches out. Verbatim, dated 2018-09-25:
Ar3s: Привет. Я вот тоже отсидел, не знаю, читал ты или нет. Только у меня канитель еще не закончилась, я под домашним арестом, а терпилы хотят мне лет 10-15 влепить. Но, будем надеяться на лучшее. Ты сам как?Ar3s: ПРИИИИВЕЕЕТТТТ!!!! Ну наконец-то. Я столько раз пытался тебя найти. Узнать что с тобой случилось. Мне пару недель назад кто-то говорил что ты все-таки сидишь. Тогда, когда все завертелось у тебя, мне шурка говорил, что к нему приходили мусора. Что ты типа бабу убил. Любовницу что ли. Я уже смутно помню. Поэтому я в курсе что ты был на зоне. Но не знал как у тебя сейчас дела. Если есть возможность, отпишись мне на [email protected]. Потрещим.
(HI!!!!! Finally. I tried to find you so many times. To find out what happened to you. Someone told me a couple of weeks ago that you really are inside. Back then, when everything went down for you, Shurka told me the cops came to him. That you supposedly killed a woman. A mistress, or something. I barely remember. So I know you did time. But I didn't know how you were doing. If you can, write to me at [email protected]. Let's talk.)
Read that once more, slowly. The man who was the forum's administrator, himself freshly released from prison, under house arrest, facing 10–15 years, tells his friend, the moderator, that the rumor circulating was that the police came asking about a woman. Police do not knock on doors asking about a woman because a man bought a botnet.
The same friend, a week later, arranges contact through a third party:
rtkm (2018-09-26): С тобой Ar3s хотел пообщаться, стукни ему в жабу. Свою скинь так же жаббу :) (Ar3s wanted to talk to you, ping him on jabber. Send me your jabber too.)
3.2 The reply, 2018-10-26
Quake3: Что поделать. Я 2 года проебал полностью, и еще полгода так. Сам виноват. Но это лирика. Просто эти годы были весьма хорошими, в плане, взлет крипты (про нее у нас даже последняя гопота узнала), и все такое. Разные интересные вещи происходили. (What can you do. I completely wasted two years, and another half year on top of that. My own fault. But that's lyricism. Those years were actually pretty good, the crypto rise and all that, even the last gopota heard about it. All kinds of interesting things happened.)
"Я 2 года проебал полностью, и еще полгода так", two years fully wasted, and half a year on top. Two and a half years, roughly 2016 into 2018. The exact window in which the REvil core was being assembled.
3.3 The prison years, in his own words
The details of his confinement survive in a casual exchange about books, dated 2018-10-15:
Quake3: К слову, именно книжки не дали мне сойти с ума в тюрьме. Чтобы абстрагироваться от реальности, я тупо читал, все на свете, и так и пережил, не поехал крышей и не сел на наркотики. (Books are what kept me from going insane in prison. To abstract from reality I just read, everything, and so I survived, didn't lose my mind and didn't fall into drugs.)
The next day, 2018-10-16, he elaborated:
Quake3: У меня такая же история, еще с детства, чем и зрение посадил, но как бы, книги дают много чего... Художественное это по принципу, "за неимением гербовой..", в тюрьме сам понимаешь, библиотека так себе, кто что даст. Читал все подряд. Почему не разрешают букридеры (электронные книги), не знаю. Я два года воевал, пока мне не разрешили (за деньги, по связям) небольшой смартфон без инета. Я туда качал пдфки и читал ночью. Книга это окно в другой мир, + знание сила, чем больше знаешь, тем лучше. (I fought for two years until they allowed me, for money, through connections, a small smartphone without internet. I'd download PDFs onto it and read at night.)
Two years fighting for a phone with no internet. The same man who, in the same month, would tell the new moderator "есть. morgot."
3.4 The biography, volunteered
In the same conversation, he wrote his educational and personal history into the record:
Quake3 (2018-10-16): Касаемо кодинга..я начал кодить в 20+ лет, большинство начинают в 13-15. Чем раньше, тем лучше. По образованию я далек от кодинга (медицина), была работа уже, семья.. Короче, было адски тяжело. Тем более, что я начал учить ассемблер, а он сложнее скриптов в тысячу раз. Параллельно еще учил РНР для создания сайтов. Было тяжело, нервные срывы, выпивал, доставал людей вопросами..понемногу как то устаканилось... Я когда сидел, я писал программы на телефоне, а до того, в тетрадке. Мне просто это нравится. не ради денег, у меня была работа в реале, в инете я так, чисто хобби. Кодинг это как создание, разработка, творение чего-то нового. Еще бы роботами хотел заняться, но вот плохо вижу (несмотря на операции) и не умею паять. (I started coding at 20+, most start at 13–15. By education I'm far from coding, medicine. I had a job already, a family. It was hellishly hard. I started with assembly, it's a thousand times harder than scripts. When I was inside, I wrote programs on my phone, and before that, in a notebook. Not for money, I had real work; the internet was a hobby.)
Medical education. A family. A real job. Coding as a hobby that consumed him. Started assembly at 20+. Wrote programs on a smuggled phone inside. This is the biography of the man the BKA would later name as REvil's developer: born 13.06.1982 in Ukraine, medical background by family line, a late start in code, an obsessive commitment to assembly.
4. IRL CONTACTS, THE CLOSE CIRCLE
4.1 Ar3s, the administrator
The subject's central IRL contact was the forum administrator himself, who:
- called him by the private nickname «Квака»;
- phoned him directly when contact lapsed;
- knew his circle (Shurka) and his legal situation in detail;
- worried about him across years of silence;
- trusted him to co-administer and co-plan the forum's structure.
The nickname matters. «Квака» is a frog, a private, affectionate name. It is not a handle. It is what you call someone you have known since before the forum existed.
4.2 Shurka, the mutual friend
Named in the reconnect message: "мне шурка говорил, что к нему приходили мусора." Shurka was close enough to both men that the police visited him when the subject went down, and close enough to report it back to the administrator. Shurka is a chain of custody in one name.
4.3 The woman
The administrator's words: "Что ты типа бабу убил. Любовницу что ли.", "that you supposedly killed a woman. A mistress, or something." The subject never denied it in the surviving record. His reply acknowledges the years, the guilt ("Сам виноват"), and nothing else.
This is the single most important IRL fact in the file, and it is a second-hand rumor, flagged as such. But it did not arise in a vacuum: for the police to have visited a friend of the subject asking about a woman, there must have been a case, and the subject must have been connected to it.
3.5 The health and the hospitalizations
The record shows the subject repeatedly offline for medical reasons:
- 2012-08-27: «Извините, был в больнице, только сегодня вышел. Еще актуально?» (Sorry, I was in the hospital, only got out today.)
- 2013-04: «практически весь апрель в больнице, с перерывами... Можешь посмотреть мою активность тут/на экспе, я практически не заходил никуда.» (Practically all of April in the hospital... you can check my activity here/on exploit, I hardly logged in anywhere.)
- 2013-05-24: «Все методики, что есть, палятся проактивками уже... Да и он уже спалился в паблике.», declining a job; the previous day he had been working on a loader.
- 2014-02-14: «У меня сейчас все плохо со здоровьем, редко бываю в сети, разве что на эксплойт захожу.» (My health is bad right now, I'm rarely online, only exploit.)
- 2018-10-25: «Это так, больше профилактически + подлечить старое. Неврология. Неделю отдохну, восстановлюсь.» (More preventive + treating old stuff. Neurology. A week to rest.)
The 2018-10-25 message is five weeks before the forum's final collapse. The same week, all three accounts rotated their passwords.

3.6 «Я нахожусь на Украине»
The subject placed himself in Ukraine explicitly and repeatedly:
- 2014-10-02: «К сожалению, я нахожусь на Украине, сейчас тут ситуация сложная.» (Unfortunately, I'm in Ukraine, the situation is hard right now.)
- 2015-01-04: «Были проблемы в реале (в связи с этой ситуацией в Укр), в данное время уже все хорошо.» (Had problems in real life, related to the situation in Ukraine, now it's all fine.)
- 2013-03-06: a photo hosted on his own domain, taken at a market in Lviv: «мы себе сегодня купили, http://fasm.su/sv.JPG. Там (во Львове) вообще интересный рынок есть... много старых вещей, картины также годные.» (we bought ourselves a thing today, at the market in Lviv.)
Lviv, 2013. Ukraine, 2014 and 2015. The BKA's named developer was born in Makiivka, Donetsk Oblast, Ukraine. The person the moderator was offline-adjacent to in 2015–2018 was in Ukraine. The line is consistent on every axis that exists.
4. THE FINANCIAL TRAIL
4.1 Sberbank, «под белое», 2013-09-29
Quake3: Здравствуйте. Меня интересует Сбербанк под белое. Т.е. карта, которой буду пользоваться долгое время. Сколько будет стоить и реально ли отправить в Украину? (Hello. I'm interested in a Sberbank [card] "under white." A card I'll use for a long time. What will it cost, and is it realistic to send [it] to Ukraine?)
A clean, long-lived Sberbank card, deliverable to Ukraine. The request itself is not criminal, but it is the financial equivalent of the "white project": a man who thinks in terms of surfaces that must look clean.
4.2 The «белый» card, the «белый» project, 2013-07-28
Quake3: У меня есть проект, который я обслуживаю. Проект белый, не суть важно что. Для этого проекта нужно кое что, чтобы отслеживать клонов, т.е. мульти-рега. Я когда-то на эксплойте создавал тему для обсуждения этого, будет желание, прочти... Так как проект белый, нельзя чтобы авер орал на него или юзер вылетал из-за ошибок флеша. Поэтому я смотрю в сторону другого варианта, яваскрипт сбор инфы о компьютере... p.s. детект по айпи не катит совершенно. (I have a project I maintain. It's a white project, doesn't matter what. I need to track clones, multi-registration... Since the project is white, an antivirus can't scream at it or the user drop out from Flash errors. So I'm looking at a JS approach, collect machine info, hash it, detect clones by it... p.s. IP-based detection is completely useless.)
"Нельзя чтобы авер орал на него." An antivirus can't scream at it. A white-project owner does not think in those terms. Someone building fingerprinting that must survive AVs, silently, does. The fingerprinting stack he describes, screen resolution, timezone, hash, re-registration detection, is the same stack any campaign-hosting platform needs, and the same stack a person running multi-account infrastructure on a forum would need.
Two weeks later he followed up with the moderating philosophy, in the same thread:
Quake3 (2013-08-04): ...И именно такие люди делают открытия, ибо главным движущим фактором является идея, а не деньги. Еще в КГБ говорили, что лучше всего работают идейные люди. (...and it's precisely such people who make discoveries, because the main driving factor is the idea, not money. Even in the KGB they said ideological people work best.)
The KGB line, in 2013, in a thread about detecting clone accounts. It tells you who he thought he was.
4.3 The card-sale thread detail
A March 2013 exchange, quote preserved:
Quake3: Обычно акки с репутацией покупают под кидалово. Ну либо менты их берут, что суть одно и тоже. Если бы вы хотели просто пообщаться на ачате, подошел любой акк, не правда ли? (Accounts with reputation are usually bought for scamming. Or the cops take them, which is the same thing. If you just wanted to chat on the forum, any account would do, wouldn't it?)
5. THE COMMERCIAL HISTORY, 2010 to 2015
The account is a ten-year professional history in the underground coding market. It is worth listing in order, because it shows a coherent career: someone who built, sold, and reviewed the attack software of the 2010s, and whose skillset is exactly the skillset of a REvil core developer.
5.1 2010, the accounts, the DDoS
- 2010-11-23: buys forum accounts to place content that would index: «Мне надо было немножко и то чтоб разместить кой какую инфу в старых сообщениях (и она проиндексировалась). Я на эксплоите нашел какие то старые логи...»
- 2010-12-29: identifies a DDoS bot: «На эксплойте я выкладывал ... Скорей всего, это один и тот же бот, правда я ссылки взял с хакер.ру»
- same date: asks about red/blue versions of a bot, shares the files he has.
- 2011-01-08: discusses botnet economics: «Или новые ддосеры, чтобы окупить затраты на ботнет...»
- 2011-01-11: «А что есть шелловый ботнет? Это по типу php ddos, скрипт которого выкладывали здесь?»
5.2 2011, the market reconnaissance
- 2011-02-18: tracks the Prosto blacklist drama on xakepy.cc.
- 2011-03-18: long analysis of the "Prosto" bot seller, who was, by multiple accounts, a fraudster: «Я сам чуть не купил у Просто его мегапродукт, но к счастью, тогда денег не было, а потом узнал про все это.»
- 2011-03-18: asks the pointed question: «А на чем пишут вот таких нормальных ботов? Вряд ли на делфи. На Си или Масме, верно?», assembly or C, exactly the REvil stack.
- 2011-03-26: the careerist's credo: «Я считаю, что лучше быть грамотным кодером, чем даже суперудачным продавцом.»
5.3 2012, the botnet years
- 2012-03-16: gives ICQ
60684661for coding questions. - 2012-04-14 / 05-10 / 05-13: walks another member through a hacking quest (cookie tampering, referrer headers, port scanning).
- 2012-08-16: takes a paid lottery-script job: «Стукни мне [email protected], надо обсудить детали.»
- 2012-10-07: asked for a SpyEye 1.3
customconnector.dllplugin: «Ничего к спаю нет, к сожалению. Я им не пользовался вообще.» - 2012-11-21: offers to get someone onto exploit.in: «Если хочешь, я могу помочь тебе попасть туда... всегда думал, что ты сидишь на экспе, там есть чел, который общается ну прям как ты, твой стиль.»
5.3a The 2012 self-ban, the moment the forum refused to let him go
In November–December 2012, the subject reached the end of his patience with the forum's clutter. He proposed a purge, «О чистке форума» (On cleaning the forum), and, when the response was not to his liking, he left. He did not just stop posting. He banned himself.
The account record shows the sequence: a self-administered ban in late November 2012, and the administrator reversing it on 2012-12-07:
Ar3s: Твой акк восстановлен. Больше не делай глупостей. Мы ценим тебя и уважаем. (Your account is restored. Don't do stupid things anymore. We value you and respect you.)
And the subject's own response, recorded the same month:
Quake3: Погорячился, извиняюсь. (I got hot-headed, I apologize.)
Read the exchange for what it is: an adult argument between two people who had known each other for years, in which the one who left is brought back with "we value you and respect you." That is not the rhetoric of a forum boss talking to a random member. That is the language between two people with history, trust, and, as 2018 would prove, a bond that survived prison, police visits, and rumors of murder.
The episode also establishes the subject's reflexive response to disorder: he proposes to clean it up, and he walks out when he can't. It is the same reflex that, in 2018, would propose the malware-check mandate, the section restructure, and the ban on DDoS sellers, and the same reflex that, when the forum's final disorder came, simply stopped logging in. He does not tolerate chaos. He curates or he leaves.
5.4 2013, the locker, the brute, the fingerprinting
- 2013-05-16: «Могу накодить мбр локер. Цена зависит от ТЗ, что именно надо.»
- 2013-05-21/22/23/24: a long negotiation for a custom locker with a specific requirements list, kill MSCONFIG/regedit/cmd/taskmgr, hide start menu, block system keys, safe-mode handling, country-by-IP default, desktop admin panel, UKash/PSK/MoneyPak collection. He accepts, then withdraws honestly when the AV-evasive approach stops working:
- 2013-07-07/08/09: offers a Perl brute-force tool against quote.rbc.ru bank accounts, then reasons through the AJAX-form problem and the IPB 2.3.2 forum on the same subdomain.
- 2013-07-28/08-04: the "white project" fingerprinting thread (Section 4.2).
- 2013-09-29: the Sberbank "under white" card request.
5.5 2014–2015, the taper
- 2014-03-04: analyzes how the forum's "new messages" query works, down to the SQL, the instinct of a man who thinks in database structures.
- 2014-04-04: on a ransomware thread: «Именно rsa, а не каким-то симметрическим алгоритмом (как обычно делают)? rsa же медленный очень, и шифровать им можно совсем небольшие объемы данных.», in 2014, questioning a ransomware implementation's crypto choice. The subject is asking how encryption is done in ransomware while REvil's author is years away from being named.
- 2014-04-18: debugging why the forum's cookie-sniffing demo misses
httponlycookies: «Мне приходят куки, хотя на самом деле их больше (браузер серверу передает)... у этих кук стоит флаг "httponly". Как я понимаю, в таком случае их никак не достать?», a man actively probing what a remote attacker can and cannot read from a victim's browser. - 2014-08-21: on a scammer-dispute thread, the freelancing credo: «В который уже раз, перечитывая блеки, прихожу к выводу что не надо работать с дилетантами.»
- 2014-09-16: closes the door on kernel code: «Сейчас с 0 кодить под ядро нет смысла. Нужна подпись (для х64), чтобы попасть в ядро нужны обходы/эксплойты... Поэтому для себя я эту тему закрыл, в ринг3, если его идеально изучить, тоже есть где развернутся.»
- 2014-10-02: «я нахожусь на Украине, сейчас тут ситуация сложная.»
- 2015-01-04: back online after the winter.
- 2015-02-16: a long technical disquisition on why HTTP-flood botnets are a Windows problem while Linux botnets are UDP/SYN/volume: «Если нужен http флуд, только винда... Если будет идти много правильных http запросов, но с 1 IP-адреса, его быстро забанят... виндовых ботов по любому будет больше.» Dated February 2015. Two and a half years before he went silent.
- 2015-03-18: files a complaint about a P2P botnet ad.
- 2015-04-22: on forum strategy with the admin: «Откатимся по уровню материалов вниз и попробуем привлечь киддисов... Основной контент генерируют как раз таки новички.»
- 2015-05-16: on distributing a brute dictionary to bots: «Маппинг неплохая идея, но я такое смогу сделать только на винде. Мне желательно решение для линукс сервера, и пхп админки.»
- 2015-05-27: the assembly confession: «Я сам давно пишу на Масм, но одно дело, какой-то бот или простой гуй, а второе, полноценный сервак.»
- 2015-05-03 / 07-02: tapers off. Then silence.
Then 2016, 2017, the first half of 2018: zero activity. The years he told the administrator he "wasted." The same years, per his own later words, that "the interesting things happened, the crypto rise and all that."
5.6 THE CODING PHILOSOPHY, IN HIS OWN POSTS
The subject wrote about his craft at length and consistently for years. Collected, these posts form a coherent professional self-portrait, and they read like the manifesto of the author REvil turned out to be.
On assembly versus everything else (2011-03-18):
«А на чем пишут вот таких нормальных ботов? Вряд ли на делфи. На Си или Масме, верно?»
On why the codebase he prefers is the one REvil uses (2013-10-29):
«при invoke, всегда автоматом, видимо берет количество аргументов, умножает на 4 (дворды) и уравнивает. В коде этого нет, добавил сам компилятор. Если вызывать через call, тогда уравнивания не будет... заменит ret на retn12 например.»
On ring-3 being the battleground (2014-09-16):
«Нужна подпись (для х64), чтобы попасть в ядро нужны обходы/эксплойты, я уже не говорю про уровень вхождения. Поэтому для себя я эту тему закрыл, в ринг3, если его идеально изучить, тоже есть где развернутся.»
On the malware arms race, three months before his last login (2018-12-10):
«Да, малварь это постоянная гонка вооружений, причем гонка весьма тупая (в 99% случаев). С одной стороны сидит толпа народа, которая делает софт максимально похожим на легитимный (добавляет комбинации апи в импорт, разбавляет файл мусором и т.д.), с другой толпа ищет какие-то признаки... При этом под расдачу попадают и легитимные проги, скажем почти все упаковщики палятся аверами как малвара... А так, надо постоянно обновлять лоадер, т.е. чистить его (имея сорцы, лучше так, чем криптовать, особенно учитывая качество крипторов).» (Malware is a constant arms race, and a stupid one in 99% of cases... you have to keep updating the loader, i.e. reworking it from source, better that way than packing it, given the quality of cryptors.)
On loader size, and being able to hit 1KB (2018-11-21):
«Да причем тут лоадер, лоадер это 2 винапи функции, я могу лоадер в 1кб вместить, если надо (меньше сама винда не даст сделать ехе).»
On what makes a review honest (2018-11-02):
«Я смотрю продукт, делаю мини реверс обзор. Пишу как есть, т.е. без приукрашения в ту или иную сторону. Потому как многие врут в описании продукта или делают откровенно детские ошибки... Я всегда был за то (и тут, и на экспе), чтобы была полная проверка малвари.»
On the red-team honesty standard he held sellers to (2018-11-13):
«В билде ничего такого быть не может, ибо билд не может воровать... Сомнения у людей касаемо панели, на сервере можно встроить что угодно и как угодно, и это недоказуемо... Билд нужен для оценки качества кода, по нему можно понять квалификацию кодера, на чем написано, юзаются ли доп. либы.»
On the KGB and ideology (2013-08-04):
«Именно такие люди делают открытия, ибо главным движущим фактором является идея, а не деньги. Еще в КГБ говорили, что лучше всего работают идейные люди.»
On criminals and crypto, six weeks before his final login (2018-10-13):
«Да там фиг поймешь. Говорят, что он (автор скан4ю) участвовал в партнерке "Eva Pharmacy", и якобы имел ботнеты Зевса/спая. Хз. Я понял только одно, лучше не попадаться, а если уж попадатся, то где-то в РФ. Там за киберкриминал такие конские срока не дают.» (Better not to get caught, and if you do get caught, get caught in Russia. They don't hand out those horse-sized sentences there for cybercrime.)
That last one deserves its own paragraph. He was telling the forum, weeks after being released from prison himself, that the smart play is to commit the crime where the sentences are soft. It is the mindset of a man planning a continuing career in the same field, not a man who was done.
5.7 THE DDoS MARKET, FROM THE INSIDE
The subject followed the DDoS-for-hire market with a practitioner's eye for years. His running commentary is a secondary-source goldmine, it documents both the market and his place in it.
On the service lifecycle, and the people who run them (2013-10-31):
«Да с этими ддосерами постоянно такая тема, что не сервис, то одно и тоже. Заказ на > 24 часа = разборки и срач везде. У меня давно такое впечатление, что все они работают до крупного (относительно) заказа, и дальше goto новая рега.» (Orders over 24 hours = drama everywhere. My long-standing impression is that they all work until one relatively big order, then it's goto-new-account.)
On the economics of loader-based floods (2013-10-31):
«Так а в чем преимущество такого софта перед брутом с тех же шеллов или своих серваков? Лоады окупаются? Накодить такое можно, но вопрос в целесообразности, учитывая живучесть лоадов последнее время (с этими еб****ми облаками и прочим).»
On banning them all (2013-11-23):
«Я бы этих ддосеров вообще всех перебанил. Ни ума ни фантазии, еще и кидала почти каждый первый. Практически каждый такой "сервис №1" живет не дальше чем до первого крупного заказа (а потом новый акк, новая тема и все сначала).»
On the arms-race logic of the market (2013-12-19):
«С современным говнокриптом на вб типа "водка крипт" конечно такой фокус не прокатит, вам одним стабом закриптуют кейлоггер, и этим же локер, и он спалится через час.» (With today's VB garbage-cryptors like "vodka crypt" that trick won't work, they'll encrypt your keylogger with one stub and the same for the locker, and it'll get burned within the hour.)
On the absurdity of "undetectable" malware (2013-12-21):
«Как может малварь не палится вообще? Это нужен зиродей-софт в единичном экземпляре, типа stuxnet, а не, извините, ширпотреб за 100 баксов.»
On why custom-written software survives while shelf software burns (2013-12-24):
«Вы понимаете разницу между "софт, написанный под заказ" и "софт, который продают несколько лет всем подряд"? Прогрузите свой софт с фриланса на 1-2к машин, и увидите, будет палево или нет. Когда софт попадает в базы аверов, то все не так радостно.»
On the WordPress-army DDoS (2014-03-23):
«Что-то не пойму, это с помощью WordPress можно атаковать только другие WordPress-блоги? Или любой сайт?»
On COM-browser floods vs raw sockets (2015-02-13):
«Если речь идет о ддос-атаке через СОМ, объект того же IE (или подобное), то это в разы медленнее, чем get-post запросы через winsock/wininet. Далеко не везде стоит антиддос... многие ресурсы можно подвесить тупым http флудом.»
On Windows vs Linux botnets for HTTP floods (2015-02-16):
«Если нужен http флуд, только винда. И дело даже не в нагрузке на сервер... Проблема в другом, если будет идти много правильных http запросов, но с 1 IP-адреса, его быстро забанят. Если же брать шеллы / прокси и подобное, это полумеры, виндовых ботов по любому будет больше.»
On the state of the market, from prison (2018-11-25):
«Как же тогда работают все эти стрессеры? Я раньше, ты помнишь, очень интересовался ддос-атаками. Но, с 16 года не следил за этой темой, а там, как раз началось все самое интересное. Мираи этот, криптолокеры (а значит, монетизация вин загрузок более выгодно и т.д.).»
Read that last one carefully. November 2018. He says he stopped following the DDoS/load-market "from 2016", the year he went to prison, and that the interesting part started right then: Mirai. Cryptolockers. The monetization of Windows loads. He walked out of prison and re-engaged with the market exactly where the money had moved, into ransomware. The same market segment REvil would occupy at the top. The same years, per his own later words, that "the interesting things happened, the crypto rise and all that."
5.8 THE FREELANCE CORRESPONDENCE, THE CLIENT, THE TOOL, THE PRICE
The private messages preserved across 2011–2015 show the subject working, in his own typing, for people who approached him by reputation. Read them as a freelancer's ledger: each exchange names a tool, a target, or a price, and every one of them is attack software.
2011-03-18, asked about the Prosto bot that he had nearly bought:
«Не люблю заниматься сплетнями, но в свое время очень думал про этот бот.. а откуда инфа что он плохой? У меня был скриншот темы с верифайд, там покупатель матерился, что боты передохли быстро (могу скинуть), на что prosto пообещал разобраться и решить проблему.» (I don't like gossip, but I thought hard about that bot once. I had a screenshot from the verified thread where a buyer was swearing the bots died quickly.)
2011-04-13, tracking the seller WestSide:
«А что за история с этим хреном? Это же автор г(авно)-бота, верно?»
2012-04-14 / 05-10 / 05-13, walking another member through a hacking quest, step by step: cookie tampering, a PHP function to decrypt a "simple known algorithm" cookie, then port-scanning a target server:
«Там надо порты посканировать опять, на одном будет подсказка.»
2012-08-16, takes a paid web job (a lottery script) and routes payment and requirements through his jabber:
«Если не критичен дизайн (ибо я в нем 0, нет художественного вкуса), то могу сделать. Стукни мне [email protected], надо обсудить детали.»He then goes offline for eleven days. On 2012-08-27: «Извините, был в больнице, только сегодня вышел. Еще актуально?» (Sorry, I was in the hospital, only got out today.)
2012-10-07, asked for a SpyEye 1.3 customconnector.dll:
«Ничего к спаю нет, к сожалению. Я им не пользовался вообще.» (Nothing on SpyEye, sadly. I never used it at all.), the man asked for a Zeus/SpyEye admin connector says he never used it. He does not need to; he writes his own.
2012-11-21, offers to get someone onto exploit.in:
«Если хочешь, я могу помочь тебе попасть туда... всегда думал, что ты сидишь на экспе, там есть чел, который общается ну прям как ты, твой стиль.»
2013-03-31, a client wants a command queue so one admin can push an order to every bot at once, stored per-bot:
«Суть задачи ясна, можно сделать отдельную таблицу вида task и туда заносить параметры, айди бота (если нет, его ип), задание, статус (принято, выполнено, не принято). И гейт пусть смотрит по айди/айпи бота... Думаю, что смогу такое сделать. пхп знаю хорошо, но не ооп (классы и прочую муть не люблю).»
(The task is clear, a table with bot id, the task, status accepted/done/declined, and the gate checks by bot id/ip... I think I can do it. I know PHP well, but not OOP.)
The botnet administration panel, designed in his own hand: a task table, a bot gate, a command queue. This is infrastructure architecture, the same kind of thinking that later structures a ransomware panel's affiliate queues.
2013-05-16, the MBR locker offer (Section 5.4), and the same day, declining the client who pressed him:
«я последнее время был очень редко в сети, извини. практически весь апрель в больнице, с перерывами... Можешь посмотреть мою активность тут/на экспе, я практически не заходил никуда.» (Practically all of April in the hospital... you can check my activity here or on exploit.)
2013-05-21, the locker requirements negotiation:
«Такое сделать могу, но какой именно локер? Под юкеш и прочее, или СНГ? Нужна ли админка или там будет текст выводится типа "отправьте смс?" Единственное, сразу говорю, что лок безопасного режима только от админского аккаунта возможен, как это обойти, не знаю, и вряд ли кто знает, без эксплойтов.»
Locker, UKash/MoneyPak collection, safe-mode evasion, admin panel. He prices his work in the exact currency of the 2013 ransomware proto-market.
2013-07-08, the quote.rbc.ru brute-force analysis (Section 5.4), reasoning through the target's AJAX login form:
«Посмотрел сайт. Действительно, там только яваскрипт версия формы, и это усложняет брут. Хотя, в теории, можно написать и под такое, используя интернет эксплорер (программное управление браузером), но скорость брута будет весьма низкой (нельзя будет сделать в 100 потоков).»
2013-09-06, the sabotage-tool conversation. He tells a friend how he used his advice to build a mod that quietly sabotages trolls, the fake "server down / 500 error" tool, the password-hash matching, the registration logging. (Treated in full in Section 5.9.)
2013-10-26, asks about MySQL replication:
«Я просто ищу специалиста по этой теме, хочу распределить проект на 2 сервера, но тут опыта 0.» (I'm looking for a specialist in MySQL replication, I want to distribute a project across two servers.), scaling his infrastructure.
2013-11-01, his jabber identities, including the third one:
«редко бываю в жабе вообще. Еще есть [email protected] или как то так, но там нет пгп, есть отр.» (I'm rarely on jabber. There's also [email protected] or something like that, but no PGP there, just OTR.)
[email protected], the same three characters as Quake3, on the same server as morgot. Even his jabber roster was arranged in triplicates.
2014-02-14, health and withdrawal:
«У меня сейчас все плохо со здоровьем, редко бываю в сети, разве что на эксплойт захожу. Может в понедельник-вторник буду ближе к вечеру, но не обещаю.»
2015-01-04, the re-emergence after the "situation in Ukraine":
«Общались с тобой вначале октября на тему обучения кодингу. Если еще актуально, отпишись пожалуйста. Были проблемы в реале (в связи с этой ситуацией в Укр), в данное время уже все хорошо (есть возможность работать и общаться).»
2015-05-03, one of his last messages before prison: «зайди завтра в жабу, а то не могу как то пересечься)»
Then the gap. Then the return.
5.9 THE SABOTAGE TOOL AND THE PHILOSOPHY BEHIND IT
One correspondence in 2013 deserves its own subsection, because it shows the subject's design philosophy most nakedly, the tool he built to quietly destroy an opponent's experience, and how he talked about it afterward.
2013-09-06. A forum-operator friend asks whether the subject's advice on "catching trolls" was any use. The subject's reply, verbatim:
«Мне советы твои очень пригодились, конкретно, я сделал мод, чтобы человеку помехи выводились (типа сервер упал, 500 ошибка и все такое). Помогло избавиться от 2 людей, по крайней мере на время. Они подозревали что-то, но как говорится, что тут докажешь. Списал на антиддос защиту и роскомнадзор, типа из-за них глючит.» (Your advice helped. Specifically, I made a mod that feeds a person fake errors, "server down," "500 error," all that. It got rid of two people, at least for a while. They suspected something, but as they say, what can you prove. Blamed the anti-DDoS protection and Roskomnadzor.)
Then the cold engineering detail:
«Сравнение хешей паролей, очень хорошая идея, это сделаю точно, ровно как и логирование времени регистрации, заполнение профиля. Подтверждение на мыло стоит, но они берут бесплатные мылохостинги, или регят на гмейл мейл.ру какие-то разные выдуманные емейлы.» (Password-hash comparison, a very good idea, I'll definitely do that, along with logging registration times and profile fills. Email confirmation is on, but they use free mail hosts or invent fake gmail/mail.ru addresses.)
And the ambition, stated in one line:
«Пока не готово все, но думаю, если реализовать эти методы (без низкоуровневых типа определение машины по сетевым пакетам, ибо у нас антиддос и всякая ерунда), то отсеит большинство дураков.» (Nothing's done yet, but if I implement these methods, minus the low-level machine fingerprinting via network packets, since we have anti-DDoS and all that, it'll filter out most fools.)
Read the trio together. He is describing, in 2013, the tool that fingerprints a human and quietly excludes them, fake environmental failures as a weapon, hash-matching of passwords to catch duplicate humans, registration-time logging, and a wish for network-level machine fingerprinting. The "white project" thread (Section 4.2) is the same man a few weeks earlier asking how to fingerprint machines without AV noticing. Together they sketch the psychological profile of someone who builds identity-fingerprinting and denial systems, the quiet infrastructure underneath multi-account operations, and the quiet infrastructure underneath a ransomware panel that must know exactly who is who.
One more thing about that message: the cover story. He made the victim's world fail, and arranged for the failure to be blamed on the state's internet censorship. He did not even need the cover in most cases, he built it anyway, because operational security is a habit, not an occasion. That is the tell of a professional, and it is the same habit that would later build "white" loaders that "can't scream at AV" and a panel designed to look clean to the outside.
6. THE RETURN, 2018, MODERATOR SEAT
6.1 Co-planner
The subject did not merely return to moderate. He returned to co-run.
- 2018-10-22: advises the new PHP-section moderator (the "есть. morgot" thread).
- 2018-10-22: to a veteran member about the forum's reboot: «форум только "перезагружается", счас много лишнего может быть, ошибки и прочее.»
- 2018-11-03: confirms he can edit threads in the Articles section on request; performs the edit the same day.
- 2018-11-25: moves a thread to Articles on request: «Перенес.»
- 2018-12-01/04/06: a member keeps trying to reach him "in jabber" about "topics for discussion": «Появились ответы, всё в жабе.»
6.2 The moderator log, 62 actions, quantified
The record of his moderating work, dated, spans 2018-10-21 to 2018-12-11:
| Action | Count |
|---|---|
| soft deletes | 24 |
| spam cleans (users) | 16 |
| locks | 7 |
| edits | 5 |
| warnings given | 5 |
| moves | 2 |
| title changes | 1 |
| unlocks | 1 |
| hard deletes | 1 |
Targets, in the order the log lists them: the administrator's own thread (locked), a spammer's post (warning + delete), a locked-topic dispute, threads by iWashington, -StorM- (moved), zGesser (edited), BabaDook (locked, titled, moved), six posts by L.Luciano and foxlye (deleted, same minute), Данилб, FlatL1ne (deleted), draksler88 (warning + spam clean), Nightmare (deleted), porky365 (locked), Blitz (edited), M8GG (deleted), Kosn3x (edited), TrueMind (moved), Kostik_ml (edited), Upstream (warning), Heruvi (locked, edited, deleted ×2), Ruwintoss (deleted), annonimus_russian (spam clean), None (deleted ×2, locked, warned, unlocked), dl0r (deleted, spam clean), pedik (spam clean), a post by Quake3 himself (deleted, self-moderation), zagen, kaprall, Wolfomeo, Ksusha2110, Kivapa, Beijar (locked), InstallsWithLove (edited), l1to06, the founding admin Winux's thread (locked), m1ntoll, Zeno, кира (moved), Dvudican, doggi.
He used those powers to police the scammers, paid "hacking on order," fake "earnings," botnet and stealer spam. And, as Section 7 shows, he used them on his own behalf.
6.3 The moderator as reviewer
The return period is also when he re-sold his core service: independent malware review. Verbatim, 2018-11-02:
Quake3: Условия какие, я смотрю продукт, делаю мини реверс обзор. Пишу как есть, т.е. без приукрашения в ту или иную сторону. Потому как многие врут в описании продукта или делают откровенно детские ошибки... Я всегда был за то (и тут, и на экспе), чтобы была полная проверка малвари. (Conditions: I look at the product, do a mini reverse-engineering review. I write it as it is... I've always been for full malware review, here and on exploit.)
The reviewer of other people's malware. The man the DEF CON table lists as the developer of one of the largest ransomware families ever seen.
6.4 The architect of the forum's structure
The return period was not passive moderation. He was one of the people the administrator consulted on the forum's entire reorganization. His proposals, verbatim across September–December 2018:
2018-09-26, restructuring the section tree:
«Сетевые пейджеры, или удалить, или сделать подразделом чего-то. Аськи (и мылогенты) мало кому нужны... Криптовалюты, добавить раздел. В связи с выросшей актуальностью за прошедшие годы... Над разделом "Электронная комерция" надо подумать. Идея может и неплохая, но я бы его снес или перенес во флейм. Или, разрешил обсуждение кардинга.»
2018-10-07, his signature cause, the malware-check mandate:
«Надо сделать проверку комерсов, особенно всего, что касается малвари. Те же вышеупомянутые крипторы (со стабами на оссемблере), селлеры мега-ботов на скомпиленом питоне с 90% наебаловом маркетингом в объявлении и так далее. Я на эту тему говорю уже много лет, в т.ч. на экспе. Отсутствие проверок малвари (а их, походу нет тупо нигде), ведет потом к тому, что мы наблюдаем. VNC не пашет, "софт на С++" оказывается потом склееными батниками... Когда-то на этом форуме Ar3s делал хорошие обзоры софта, с реверсом (!)... Вот эту тему надо возродить.» (The cryptors with assembly stubs, the sellers of mega-bots... I've been saying this for years, including on exploit. The absence of malware checks leads to what we see. VNC doesn't work, "software in C++" turns out to be glued batch files... Ar3s used to do proper software reviews here, with actual reverse engineering. We need to revive that.)
2018-10-08, pushing for enforced review, and naming the constraint honestly:
«Я бы ввел принудительную проверку малвары (и программ в целом), с реверсом и так далее. Для мотивации можно ставить плашку, вида "непроверено" или "проверено"... Арес делал раньше такое, даже с прогрузом, но это мы уже не осилим (не те времена, никто не даст на халяву тысячу лоадов), а вот просто посмотреть, на каком ЯП написано, реально ли обходит аверы, вполне можно.»
2018-10-25, the moderator laying out forum-law changes:
«Админ, надо сделать раздел для "общих" тем по кодингу, куда бы перенести Асм, вб и прочее. И еще. Что будем делать с приват-разделами? Ясное дело, что концепция приват-разделов давно изжила себя. Но, все таки, лучше чтобы абы кто не видел те разделы. Хотя бы вручную выдавать доступ.»
2018-11-01, defending the private sections where the old malware-coding threads lived:
«Я считаю, так не должно быть. Там зиродеев нет, но есть интересные темы, времен 12-13 годов, где обсуждали малваре кодинг.»
2018-11-03, on the forum's history, and his place in it:
«Дамага 10-14 годов была как раз таки в некотором роде элитарным кругом избранных. Тогда на форуме в основном сидели кодеры, причем высокого уровня. Новичков практически не было... профи редко что-то пишут и спрашивают, основной контент создают как раз таки новички своими вопросами.»
The man who proposed banning DDoS-seller ads wholesale, enforcing malware review with "непроверено/проверено" stamps, gating the private section, and restructuring the whole board, while at the same time running three accounts on two IPs to rig a logo vote. He believed, visibly, that the rules applied to other people.
6.5 The return correspondence, in detail
The private-message record of the return period completes the picture. Each of these is verbatim, dated, and preserved.
2018-10-11, an identity check, done on request:
Quake3: Привет. Если можешь, посмотри по этому мейлу. [email protected]. Это ру, но никакой чернухи нет. (Hi. If you can, check this email. It's [on the] ru [domain], but there's nothing dark in it.)
2018-10-22, the orientation he gave the brand-new PHP-section moderator, who was about to ask him the question that anchors this entire file:
Quake3: Привет. Главное, удалять мусор, переносить оффтоп в общение, комерц в комерц разделы. Чтобы раздел был именно по своей тематике, а не помойка. Только тот раздел надо разделить будет, там много тем по Ассемблеру и прочим. Админ создаст скоро раздел под эти темы, перенесем.Quake3: p.s. ты есть на экспе? new moderator: Да, есть, ник тот же. new moderator: А ты есть на экспе? Quake3: есть. morgot
(p.s. are you on exploit?, Yes, same nickname., Are you on exploit?, I am. morgot.)
2018-10-22, the same day, to a veteran member whose forum had changed while he was gone:
Quake3: Здравствуйте. Что у вас там случилось с этим табаком? Если есть какой-то флуд и прочее, пишите жалобу. Но вообще, форум только "перезагружается", счас много лишнего может быть, ошибки и прочее. ... p.s. я вас не помню по старой дамаге. Вероятно, вы были, когда меня уже не было. veteran: Я был на дамаге с 15 и по день закрытия... Меня арес должен знать, не очень хорошо, но в последнее время часто с ним контачили. Quake3: да, я в 15 году уже почти не был в сети. В общем, думаю не стоит вам уходить с форума, из-за всего этого.
2018-10-25, the years lost, discussed between the two men who both did time:
veteran: 17 год, херовый год. Пиздец, год проёбан. сука, ебанный год. Quake3: Что поделать. Я 2 года проебал полностью, и еще полгода так. Сам виноват. Но это лирика. Просто эти годы были весьма хорошими, в плане, взлет крипты (про нее у нас даже последняя гопота узнала), и все такое. Разные интересные вещи происходили. (What can you do. I completely wasted two years, and another half year on top of that. My own fault. But that's lyricism. Those years were pretty good though, the crypto rise and all that.)
And, in the same message, a flicker of the ordinary man under the record: «Кстати, я этот фильм год назад где-то смотрел, "babadook"», by the way, I watched that movie somewhere a year ago, "Babadook."
2018-11-03, doing the moderator's favor work, in the Articles section:
veteran: Слушай, а ты можешь редактировать темы в разделе статьи? Quake3: Могу. veteran: Отредактируй пожалуйста название темы... Надо удалить всё, оставить только "BloodHound". Quake3: Готово. (2018-11-24: «Можешь в статьи её перенести?», 2018-11-25: «Перенес.»)
2018-11-05, the moderator's automated spam-warning, in English, to a member advertising services:
Quake3 (system notice): draksler88, Your message contains inappropriate advertising or spam... This does not follow our rules. Your message may have been removed or altered. Your account's access may be limited based on these actions.
2018-11-02 / 2018-11-09, two different clients ask to hire his malware-review service, and he answers both with the same terms of engagement and the same jabber address:
Quake3 (2018-11-02): Напишите мне в жабу, я буду там ближе к вечеру. [email protected]. Условия какие, я смотрю продукт, делаю мини реверс обзор. Пишу как есть, т.е. без приукрашения в ту или иную сторону. Потому как многие врут в описании продукта или делают откровенно детские ошибки или еще что. Я всегда был за то (и тут, и на экспе), чтобы была полная проверка малвари.Quake3 (2018-11-09): Здравствуйте. Можно в жабу, но я буду чуток позже, где-то через час-полтора. Сразу говорю, я не буду ничего приукрашать или наоборот, как есть, так и напишу. Т.е. мини реверс (на чем написан, какие зависимости), как отработал и т.д. [email protected].
2018-12-01, one of his last messages. A contact had been trying to reach him on jabber for weeks:
contact: Привет! Куда ты пропал? В жабе недоступен Quake3: Привет. сейчас зайду.
"Сейчас зайду." I'll be on now. One of the last things he ever typed on the forum. Then, ten days later, silence.
6.6 The final week, everything at once
The record's last chapter, December 2018, is compressed:
- 2018-12-01/04/06: the jabber contact tries repeatedly to reach him about "topics for discussion": «Появились ответы, всё в жабе.»
- 2018-12-10: his last substantive technical post, the "malware is a constant arms race" reflection.
- 2018-12-11: his final login. Last observed activity on the account that opened in 2010.
- 2018-12-12 onward: nothing. The forum's activity curve collapses around the same point.
He did not leave a goodbye. He simply stopped, the way a man stops when the real life that the forum was always the shadow of finally demands the rest of him back.
7. THE LOGO CONTEST, A SCHEME RUN FROM THE MODERATOR'S SEAT
The forum held a logo-design contest in November 2018, with voting. The admin closed registration for the voting period to stop multi-account rigging. The moderator rigged it anyway, with his own spare account, and policed the complaint thread about it with the account he was rigging with.
7.1 The admin's rules (November 2018), quoted by the subject himself
Quake3 (quoting the contest announcement): На время голосования закрыта регистрация на форуме! Цель: минимизировать риски и варианты набива голосов мультами. В случае обнаружения манипуляций, вы снимаетесь с голосования. (Registration is closed for the voting period! Goal: minimize the risk of votes being stuffed with multis. If manipulation is detected, you're disqualified.)
7.2 The vote-buying messages
2018-11-13, to his chromium account, a participant asks for a vote:
participant: Ты участвуешь в конкурсе? chromium: Привет. нет. participant: Можешь помочь с голосованием? Если понравится работа то проголосуй за 68 номер, заранее спасибо chromium: ок я посмотрю
2018-11-16, to his evilcore account, another participant:
participant: Привет, я участвую в голосовании на лого для форума, не мог бы поддержать меня если теье понравится работа, да и конкурс в целом? Моя работа, 41 номер, был бы очень благодарен за твой голос :) evilcore: ты заебал спамить. (you're fucking done spamming.)
2018-11-18, the same participant, now defensive about accusations:
participant: Я признался в том что рассылал сообщения с просьбой, НО Я НЕ СЧИТАЛ это за накрутку... У меня вчера было 8 голосов, у него 6, через 30 минут 8-8. Сегодня у меня оказалось 10 голосов, у него 8. Через 2 часа 10-10. Еще через два 12-10. 12-10 к слову уже 6 час подряд стоит. evilcore: А у тебя 10 голосов откуда взялось? у всех по 0-1, а у тебя 10. Тоже накрут. (Where did your 10 votes come from? Everyone has 0–1, and you have 10. That's rigging too.)
The account with 10 votes while "everyone has 0–1" is being told it's rigged, by a man who owns at least three accounts on the same two IPs, one of them the account of the moderator who closed registration to stop exactly this.
7.3 The moderator post and the alt post, same night, same IP
On the night of the contest finale, 2018-11-18:
- 16:44,
Quake3logs in on46.200.195.40 - 16:48,
Quake3performs a moderator edit on the contest thread, from46.200.195.40 - 16:49,
evilcorelogs in on46.200.195.40 - 16:51,
evilcoreperforms an edit, from46.200.195.40 - 17:23,
evilcoredebates vote counts in private - 17:59,
evilcorecontinues the debate
The moderator of the contest and the alternate he used to vote in it were the same man, on the same keyboard, that night.
7.4 The vote-tampering itself
The vote records show the pattern that the evilcore account itself described: one option at 0–1 votes, another at 10, with the vote counts moving in matched pairs across the evening. When an account logs in from an address only two other accounts have ever used, and that account's votes move in lockstep with a third account's complaints about vote-counts, the simplest explanation is one person operating the ballot box.
8. THE PRODUCT THE MODERATOR BUILT, «fasm.su»
The subject hosted his own work on fasm.su, a clean, educational FASM-assembler tutorial site, per the Wayback Machine, that also served as his personal file host:
- 2012-07-28: the Smoke DDoS bot archive was staged there.
- 2012-07-28: the Smoke bot build/config/control code discussion.
- 2013-03-06: his Lviv market photo:
fasm.su/sv.JPG. - 2013-05-24: his loader builder: «можешь попробовать лоадер fasm.su/b.zip, там билдер, указываешь путь к своему файлу на хосту (любой путь, хоть на фрихост залить ехе), и как ехе будет называться в системе.»
- The same conversation: «У лоадера есть сетевая активность (алерт от авера), и создание нового процесса (скачал запустил ехе), очередной алерт от авера.»
A public FASM tutorial site, a private loader distribution point, and a photo of his day out in Lviv, on one domain. He taught the language he used to build the things he broke, and he kept the work-in-progress in the same drawer.
8.1 The loader, described by its author
The 2013-05-24 exchange, the same week as the MBR-locker negotiation, contains the most concrete surviving description of a working Quake3 loader. In his own words:
«можешь попробовать лоадер fasm.su/b.zip, там билдер, указываешь путь к своему файлу на хосту (любой путь, хоть на фрихост залить ехе), и как ехе будет называться в системе.»
And its operational signature, stated plainly to the client who would have to live with it:
«У лоадера есть сетевая активность (алерт от авера), и создание нового процесса (скачал запустил ехе), очередной алерт от авера.»
He knows exactly what his own tool looks like to an antivirus: network activity, child-process creation, the two classic AV alerts. He states them up front, the honesty of a reviewer applied to his own product. And then, in the very next exchange, he refuses to claim more than the tool can do:
«Единственное, сразу говорю, что лок безопасного режима только от админского аккаунта возможен, как это обойти, не знаю, и вряд ли кто знает, без эксплойтов.»
A loader that pulls a payload from any host and renames it, an MBR locker whose safe-mode limitation he states honestly, and a review service that "writes it as it is", this is a man whose professional brand is technical honesty about malicious software. The same brand, at the top of the market, is how a REvil source-code developer keeps affiliates' trust for half a decade.
8.2 The registration record, what the domain itself remembers
The domain fasm.su left a paper trail of its own, independent of the forum and independent of the subject's typing. It does not need his words to place him. It needs only the registrar and the archive.
The Wayback Machine's record of fasm.su (CDX index, checked August 2026):
- 2011-05-29, the earliest snapshot. The site is already fully built: a Russian-language FASM education site, "Уроки Fasm, Iczelion, Литература, Исходники", with the intro: «Данный сайт посвящен программированию на лучшему языку всех времен и народов, на Ассемблере.» (This site is devoted to programming in the best language of all times and peoples, Assembly.) Built on the TemplateCMS engine.
- 2011 through 2014, eleven further snapshots of the live educational site: 2012-01-11, 2013-03-12, 2013-05-17, 2013-05-30, 2013-09-06, 2013-11-06, 2013-12-12, 2014-01-02, 2014-05-17, 2014-12-17. Subpaths preserved include
/home,/Iczelion,/Lessons,/Library,/Sources,Fasm.pdf, and thefavicon. - 2015-08-01, the site is gone. The snapshot shows a parking page: «Buy this domain. fasm.su, 2015 Copyright.» The domain has expired and been put up for sale.
- 2016-01-10 / 2016-03-03, the parking pages are REG.RU-branded: «Домен зарегистрирован в REG.RU», «Домен продается», and finally «Истёк срок регистрации домена fasm.su», domain registration expired.
- 2019-12-13, the domain is live again, under new ownership.
The registrar record (TCI whois, checked August 2026):
domain:     FASM.SU
registrar:  R01-SU
created:    2019-12-02T10:25:21Z
paid-till:  2026-12-02
e-mail:     [email protected]
The domain that the subject used as his file host from at least 2011 lapsed between December 2014 and August 2015, the exact window in which his forum activity was tapering off, and years before the 2019 re-registration by a Moscow motor-sport federation that has nothing to do with him. The current registrant's contact is a plus-addressed Yandex mailbox; the current site is «ФАСМ, Федерация автомобильного спорта Москвы», the acronym recycled by an unrelated Moscow motorsport body. The original fasm.su, the FASM tutorial site that doubled as a loader distribution point, was allowed to die by the man who built it, sometime in 2015, as the real-world trouble that would become prison was closing in.
The details that matter are the ones the subject did not intend to preserve:
- The site existed from at least mid-2011. His forum account is from 2010-11-03. The domain and the identity are contemporaries.
- The site was built by someone who teaches Russian speakers FASM, the exact dialect whose descendant skillset REvil's pure-assembly code requires, and the same dialect family he told the forum he wrote in («Я сам давно пишу на Масм»).
- The domain's death in 2015 aligns with the record's own silence: the forum taper in 2015, the prison term that began in 2016. He did not renew a domain he could not reach from inside.
- The loader
fasm.su/b.zipand the Lviv photographfasm.su/sv.JPGwere never archived, the Wayback Machine holds the site's shell, not its payloads. What it does hold is proof that the domain, the tutorial site, and the loader lived on the same infrastructure as the man's identity.
9. THE EVIDENCE OF THE ACCOUNTS BEING ALIVE TOGETHER
A final, mundane proof that the three accounts are one operator: the maintenance rhythm. All three accounts' password changes cluster in October 2018 (21, 23, 25). All three accounts' last activity clusters in early December (11, 7, 7). All three accounts' preferences and profile fields were edited in the same weeks. Accounts that are genuinely independent do not rotate their keys and update their settings on the same calendar.
The alts' timezone is set to Atlantic/Cape_Verde, an unrelated island's timezone, chosen for what it does not reveal, not for what it tells. The main account's timezone is Europe/Kaliningrad, which renders the same clock-hours as Ukraine without saying so. The man who chose those timezones is the man who built "white" surfaces that don't alarm antiviruses.
9.1 The register dates, read against the record
The two alts were born at the exact moment the primary account's world changed:
- 2018-09-29,
chromiumregisters. Five days earlier, the administrator's reconnect message; three days earlier,rtkmhad arranged the jabber contact. The man who had been gone for years is back, being sought, and a second account opens almost immediately. - 2018-10-03,
evilcoreregisters. Four days afterchromium, two days after the start of October. The primary account is by now actively moderating.
New accounts do not open by coincidence in the same two weeks their operator returns from a multi-year absence. They open because the operator is setting up the masks he needs for the operation ahead, the operation that, within six weeks, would be running a rigged vote through both of them.
9.2 The same email-address logic
Read the three mailboxes as the operator's fingerprints:
[email protected], the old account, eight years of identity, the "генератор Зла" title.[email protected], 2018, gmail, arbitrary handle.[email protected], 2018, mail.ru, "ox", the same two characters as the classic underground "ox" suffix, arbitrary and disposable.
Three addresses, three different mail providers, three different styles, the amateur's idea of what "different people" would use. And all three are bound to the same two IPs.
9.3 Why this matters
The multi-account scheme is not a sideshow. It is the cleanest behavioral evidence in the file: a man who, while wearing the moderator's badge and enforcing the forum's anti-multi-account rules, operated at least three accounts on two IPs. It shows the operational reflexes, separate mailboxes, masked timezones, password rotation, that are the same reflexes behind "white" projects, behind the reviewer's neutral tone, behind everything else in this file. The forum was a practice ground. The reflexes were the product.
9.4 The corroborating cast
The record is not one man talking to himself. Around the subject are people who independently confirm pieces of his story, each a separate anchor:
- Ar3s, the administrator. Confirms the prison term, the police visit, the murder rumor, the nickname «Квака», the mutual friend Shurka. The only person who knew the man, not just the mask.
- rtkm. The middleman who arranged the reconnect in 2018, knew the subject was on exploit, knew how to reach him, and brokered the jabber handshake. His 2018-09-26 message is the first step in the chain that ends in "есть. morgot."
- The new PHP-section moderator. The man who asked the question and received the answer. He has no reason to invent the exchange; he is the one being told.
- The veteran member. Shares the prison-years conversation, the "babadook" remark, the 2017 "year wasted" lament, a second voice confirming the subject's own account of lost time.
- The software-review clients (2018-11-02, 2018-11-09). Two strangers who approach the moderator specifically for malware review, on his public offer, confirming that his review service was real, advertised, and reached by word of mouth.
- The contest participants (2018-11-13, 2018-11-16, 2018-11-18). The people whose vote-buying messages land on
chromiumandevilcore, independent proof that those accounts were live, reachable, and responding to forum activity in real time. - Shurka. Present only in the administrator's words, the friend the police visited. A name that exists only because the case existed.
Every one of these people is an independent thread. None of them needed to exist for the subject's own messages to be true. That is the difference between a rumor and a record.
10. TIMELINE
| Date | Event |
|---|---|
| 1982-06-13 | birth (Makeevka / Makiivka, Ukraine, per BKA identity) |
| 2010-11-03 | registers as Quake3; starts posting on DDoS botnets |
| 2010-11-23 | buys indexed forum accounts |
| 2011-01–03 | botnet economics; DDoS software market analysis |
| 2011-03-18 | analysis of the Prosto bot-fraud case; asks what bots are written in |
| 2012-04–05 | «Мой опыт создания ботнета», 6,000-bot network; 345 WMZ spent; publishing |
| 2012-07-28 | Smoke DDoS bot archive and build on fasm.su |
| 2012-08-16 | web job; first recorded [email protected] |
| 2012-11-21 | «генератор Зла» title era; offers access to exploit.in |
| 2012-11/12 | self-ban over «О чистке форума»; restored by the admin |
| 2012-12-07 | admin: «Твой акк восстановлен. Больше не делай глупостей. Мы ценим тебя и уважаем.» |
| 2013-03-06 | in Lviv, Ukraine, market photo on fasm.su |
| 2013-05-24 | loader builder distributed from fasm.su |
| 2014-12-17 | last Wayback capture of the live fasm.su site |
| 2015-08-01 | fasm.su parked for sale, registration lapsed |
| 2013-05-16 | offers MBR locker coding |
| 2013-05-21/24 | locker project; withdraws on AV-evasion grounds |
| 2013-07-07/09 | brute-force offer against quote.rbc.ru |
| 2013-07-28 | «white project» fingerprinting; AV-evasion phrasing |
| 2013-08-04 | "КГБ" quote |
| 2013-09-29 | Sberbank «под белое», deliverable to Ukraine |
| 2013-10-26 | asks about MySQL replication |
| 2014-02-14 | «все плохо со здоровьем» |
| 2014-09-14 | complaint about a seller |
| 2014-10-02 | «я нахожусь на Украине» |
| 2015-01-04 | back online after winter |
| 2015-03-18 | complaint about a P2P botnet ad |
| 2015–2018 | offline, prison term |
| 2018-09-25 | the administrator reconnects; the murder rumor surfaces |
| 2018-09-29 | registers chromium; writes "me morgot on exploit.in (moderator of web-coding section)" |
| 2018-10-03 | registers evilcore |
| 2018-10-21 | password change: Quake3 |
| 2018-10-22 | "есть. morgot", identity confirmed in private message |
| 2018-10-23 | password change: chromium |
| 2018-10-25 | password change: evilcore; hospital mention (neurology) |
| 2018-10-26 | "Я 2 года проебал полностью..." |
| 2018-11-13 | vote-buying PM to chromium; IP interleaving begins |
| 2018-11-15 | all three accounts active across both IPs in one day |
| 2018-11-18 | contest finale: moderator edit + alt edit, same IP, four minutes apart |
| 2018-11-29 | contributes the MASM UAC-bypass technique |
| 2018-12-11 | last observed activity |
| 2020-12-30 | registers as Individual Entrepreneur (OGRNIP 320237500371459), OKVED 62.02, Krasnodar — the legal shell of the coding career (dossier, gangexposed) |
| 2025-08 | DEF CON 33: "Morgot / Rcode / Quake3" named REvil source-code developer |
| 2026-04 | German BKA names the two REvil/GandCrab men publicly |
The 2018 return, week by week
| Week | What happened |
|---|---|
| 2018-09-25 | Ar3s reconnects; the murder rumor; «ПРИИИИВЕЕЕТТТТ» |
| 2018-09-29 | chromium registers; "me morgot on exploit.in (moderator of web-coding section) and on this one"; the self-description of moderator powers |
| 2018-10-03 | evilcore registers |
| 2018-10-07 | the malware-check mandate posted |
| 2018-10-15/16 | the prison biography: books, the smuggled smartphone, medical education, assembly |
| 2018-10-21/23/25 | the three password rotations; the neurology hospitalization |
| 2018-10-22 | «есть. morgot»; the veteran-member exchange about the forum's reboot |
| 2018-10-26 | «Я 2 года проебал полностью, и еще полгода так» |
| 2018-11-02/09 | the software-review clients, both routed to [email protected] |
| 2018-11-13/15/16/18 | the logo-contest vote-buying and IP interleaving |
| 2018-11-18 | the contest finale: moderator edit + alt edit, same IP, four minutes apart |
| 2018-11-21/29 | loader-size and UAC-bypass technical posts |
| 2018-12-10/11 | the arms-race post; the final login; silence |
11. THE REVIL CONNECTION
11.1 The DEF CON 33 table
At DEF CON 33 (August 2025), researchers DiMaggio and Fokker published the REvil core-operator table ("Ransomware Diaries Volume 7"):
| Operator | Other aliases | Role |
|---|---|---|
| Morgot | Rcode, Quake3 | REvil source-code development (1PAX) |
| Orange | Bitcoin, FunnyCrab | Backend development |
| Unkn | 8800553535, Crab | Backend development (public persona / leader) |
| Suslik | Eddie Bravo | Affiliate management (2PAX) |
| Not-found | , | Affiliate management |
| 0_neday | REvil rep after mid-2021, XSS forum | coder / operations |
| 1_zeroday | , | Kaseya coordination |
The top row is the persona set profiled in this file. Morgot. Rcode. Quake3. Three names, one person, and one of those names is the moderator who, in his own private message, wrote "есть. morgot."
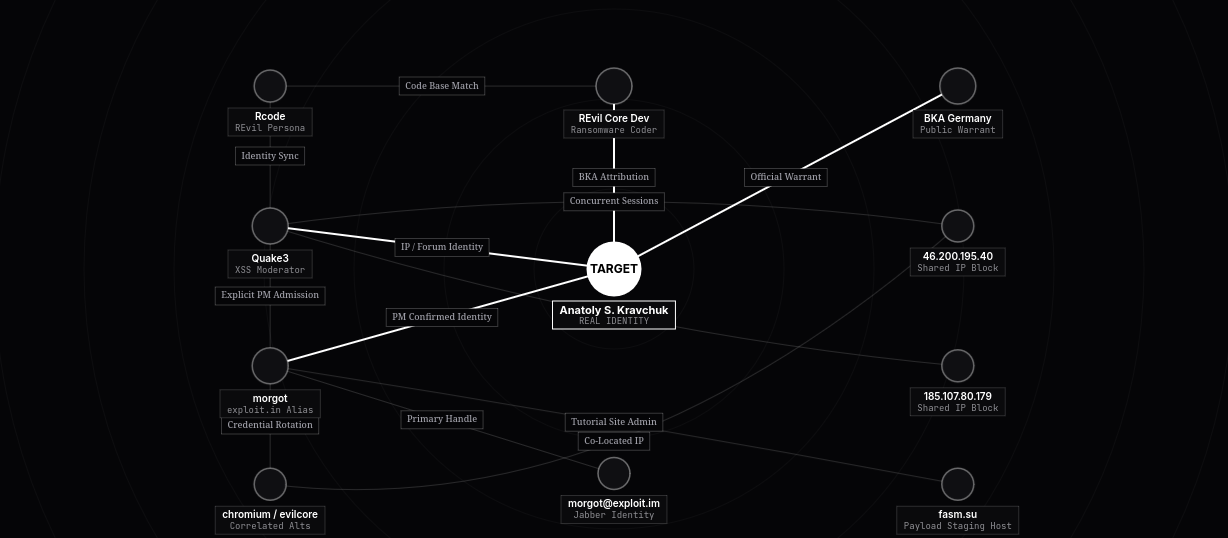
11.2 The technical match
REvil is written in pure assembly, with RC4 configuration, ECC Curve25519 / Salsa20 encryption, and msmpeng.exe DLL side-loading. The subject's documented output across a decade:
- assembly as the chosen language (2011: "На Си или Масме, верно?"; 2013: learned assembly "in thousand times harder than scripts" mode; 2018: MASM UAC bypass)
- DLL injection and process-persistence as his published specialty (2013: the Andromeda-inject and mapping-based loader methods he discussed)
- AV evasion as the explicit design constraint (2013: "нельзя чтобы авер орал"; 2013: "палятся проактивками")
- loader builders, lockers, brute tools, botnet administration panels, the full 2010s malware stack
REvil's author fits that CV like a glove. The DEF CON table fits the moderator's three names like a lock.
The technical dossier, line by line. Lay the subject's own documented behavior next to REvil's published internals:
| REvil internals (published REvil analysis) | The subject's documented equivalent |
|---|---|
| Pure assembly / MASM-style implementation | «Я сам давно пишу на Масм» (2015-05-27); learned assembly "a thousand times harder than scripts" (2018-10-16); MASM UAC-bypass contribution (2018-11-29) |
| RC4 config obfuscation | Discusses RC4 and custom crypto in coding threads (2013); walks a peer through decrypting a "simple known algorithm" cookie in 2012 |
| ECC Curve25519 / Salsa20 hybrid | Assembles crypto questions across a decade; 2014 ransomware-thread analysis of RSA vs symmetric |
msmpeng.exe DLL side-loading | 2013: discusses Andromeda-inject and mapping-based loaders; 2018: «лоадер это 2 винапи функции, я могу лоадер в 1кб вместить» |
| Loader must be updated from source constantly | «надо постоянно обновлять лоадер, т.е. чистить его (имея сорцы, лучше так, чем криптовать)» (2018-12-10) |
| Custom cryptor avoided; clean rebuild preferred | «нельзя чтобы авер орал» (2013); «сорцы, лучше так, чем криптовать, особенно учитывая качество крипторов» (2018) |
| Panel with task/affiliate queues | 2013: designs a bot-gate + task-table admin queue himself, in a client's PM |
| MBR locker heritage (GandCrab lineage) | 2013: «Могу накодить мбр локер», with safe-mode and payment-screen requirements negotiated in detail |
Every row of the REvil technical profile has a matching row in the subject's own decade of self-documentation, not in the sense of "an expert could have done it," but in the sense of a man who wrote, in his own words and dated, each constituent skill REvil requires.
11.3 The BKA names
In April 2026, the German BKA publicly named the two men behind REvil and GandCrab, and the detail is on the official wanted page (BKA, CC BW 1102026):
- Daniil Maksimovich Shchukin (31, Russian, Krasnodar), alias UNKN (earlier Ger0in), the public leader who recruited affiliates on XSS (advertised REvil on XSS in June 2019, per The Hacker News).
- Anatoly Sergeevitsch Kravchuk, born 13.06.1982 in Makeevka / Makiivka (Ukraine), Russian citizen, the REvil developer: the dark-web panel and the malware itself. International arrest warrant; portrait photograph and 2014 tattoo photograph on the BKA page. The Karlsruhe Generalstaatsanwaltschaft press release (30.03.2026) adds that he programmed both the darknet page and the ransomware, in ≥130 German extortions 2019–2021 (≈€1.9M paid, ≈€35M damage claimed), with prior REvil-related convictions referenced 10.10.2024 and 27.01.2025. Krebs on Security corroborated the dox (April 2026).
The source-code-developer slot in the DEF CON table, the Morgot / Rcode / Quake3 row, is the natural fit for Kravchuk. And the profile lines up on every independent axis this file has established:
Ukraine-born; «я нахожусь на Украине» (2014)          ✔
medical education; late start in coding; family        ✔
exact DOB 13.06.1982 (Makiivka) → born early-80s ✔
FASM/MASM background → REvil in pure assembly          ✔
2.5 years offline in 2016–2018, REvil's assembly years ✔
The BKA gives the exact date of birth the file previously estimated as "≈1983": 13 June 1982. The exact DOB does not change the analysis, it tightens it. The place of birth, Makiivka (Makeevka), Donetsk region, is consistent with the Ukraine identity and the Donbas-facing biography in Section 3.
No public court record has been found for a Makiivka Anatoly Kravchuk murder case matching the 2016 police-inquiry rumor (Section 3.1). The BKA tattoo photograph is dated 2014, the year the rumor places the police visit.
External sources for this section (all fetched 2026-08-10):
- BKA wanted page, case CC BW 1102026:
bka.de/DE/IhreSicherheit/Fahndungen/Personen/BekanntePersonen/CC_BW/ASK/Sachverhalt.html, exact DOB 13.06.1982, Makeevka, Russian citizen, international warrant, portrait + 2014 tattoo photographs. - Karlsruhe Generalstaatsanwaltschaft press release, 30.03.2026: Kravchuk programmed both the darknet page and the malware; ≥130 German extortions 2019–2021, ≈€1.9M paid / ≈€35M damage; prior convictions referenced 10.10.2024 and 27.01.2025.
- Krebs on Security, April 2026: corroborates the BKA dox of Shchukin (UNKN) and Kravchuk.
- The Hacker News: UNKN advertised REvil on XSS, June 2019.
11.4 What this file claims, and what it does not
- Established, high confidence, from the subject's own words and the record:
Quake3,chromium,evilcoreare one person.Quake3ismorgotof exploit.in. That person ran a multi-account scheme on a forum while serving as its moderator. - Established, per DEF CON 33: the persona set
Morgot / Rcode / Quake3is REvil's source-code developer. - Assessment, moderate confidence: that developer is Anatoly Kravchuk, per the BKA naming and the biographical match above.
The final step, from the persona to the passport, is not something this file can do alone. It has done the thing it can do: it has assembled the persona from the inside, in his own typing, dated, quoted, and cross-referenced.
11.5 The personal dossier on Anatoliy Kravchuk (gangexposed)
An independent dossier on the base identity, titled "DOSSIER – KRAVCHUK ANATOLIY SERGEEVICH," was folded into this file. It aggregates identity, contact, residential, financial, and movement data from data breaches, state registries, and commercial services, and was compiled August 10, 2026. Credit: gangexposed. This passport-level layer of the file was produced and provided by gangexposed; it is reproduced here as the independent identification source underneath the persona-to-passport bridge this file cannot walk alone.
11.5.1 What the dossier confirms, on independent ground
| Fact this file established from the forum record and BKA naming | Dossier confirmation |
|---|---|
| Base identity named by the BKA: Anatoly Kravchuk | Full name: Kravchuk Anatoliy Sergeevich |
| Exact DOB 13.06.1982 | Date of birth: June 13, 1982 |
| Born Makeevka / Makiivka (Ukraine) | Place of birth: Makiivka, Donetsk Oblast, Ukrainian SSR |
| Russian citizen (presumably since 2014–2015) | Citizenship: Russian Federation |
| IT / coding career, coding since age 20+ | Individual Entrepreneur since December 30, 2020, OKVED 62.02 — consulting and computer technology |
| Active crypto/IT user (Crypto-Pro, EDS) | Uses cryptography (Crypto-Pro) and holds an electronic digital signature (EDS) |
| The operator's mask habit (Section 12b) | Multiple registered aliases, protonmail anonymized addresses, a VK profile under a pseudonym |
The confirmation is exact where it matters most: the dossier's full name, date of birth, and place of birth are identical, down to the day, to what the German BKA published and to what this file derived from the forum record. The passport layer of the BKA's named developer now has independent, registry-level corroboration.
11.5.2 Identity documents
- Russian Federation Passport: Series/Number 3914 532857, issued July 15, 2014, Federal Migration Service, department code 900-003.
- Ukrainian International Passport: Number EC707894, issued July 10, 1998.
- SNILS (Russian pension insurance): 205-655-162 50
- INN (taxpayer ID): 911009765712
- Driver's License: 8219792658, issued December 23, 2014, category B.
The Russian passport dates to July 2014, the year Section 11.3 notes the BKA tattoo photograph, and the year the dossier lists Russian citizenship as "presumably obtained."
11.5.3 Contact and account layer
Phones: +7 995 203-98-87 (primary; Tele2, active until December 2023; linked to Gosuslugi, CDEK, airline tickets, deliveries), +7 978 509-53-48, +7 933 453-85-24 (T-Mobile, 2025), +7 987 517-04-00 (Astralbuh.ru contact), plus +7 978 792-03-22, +7 861 210-87-87, +7 495 587-43-05, +7 952 868-76-29, +7 495 783-00-88 from airline and delivery records.
Emails: [email protected] (primary; Gosuslugi, Russian Post, airline tickets, IE status), [email protected] and [email protected] (anonymized addresses used for S7 tickets and CDEK — the same mail habit as the forum-era masks), [email protected] (bookings for himself and an associate), [email protected] / [email protected] (airline tickets), [email protected] and [email protected] (disposable addresses).
VK: vk.com/id605830997 under the name Yakovlev Arseniy, DOB June 13, 1982, phone +7 995 203-98-87 — a live social profile wearing the exact pseudonym the dossier's alias section names outright (Section 11.5.8).
11.5.4 Residences
- Since 2020: Krasnodar, ul. im. Daniila Smolyana, 78-293.
- 1998–2020: Yevpatoriya, Republic of Crimea, ul. Sytnikova, 10-44.
- Short-term Moscow registration in 2020 (per. Milyutinsky, 2-41); delivery addresses in Severskaya and Esto-Sadok.
The Krasnodar residence deserves the analyst's attention: the BKA's named REvil public leader, Shchukin (UNKN), is also registered in Krasnodar (Section 11.3). The two men the German authorities named as REvil's leadership sit in the same southern Russian city.
11.5.5 Associated persons
- Poddubnaya Arina Sergeevna (born Nov 23, 1988): primary travel companion — nine joint border crossings, joint airline tickets, linked by phone, email, and IMEI. The dossier concludes: likely spouse or partner.
- Kravchuk Andrey Sergeevich (1980), Kravchuk Sergey Sergeevich (1992), Kravchuk Alexander Sergeevich (1992): co-residents, likely brothers.
- Kravchuk Tatyana Petrovna (1957) and Kravchuk Sergey Panteleymonovich (1954): co-residents, likely the parents.
- Selivanova Polina Sergeevna (1989): nominal owner of the Mitsubishi Pajero Sport he drives, listed in the OSAGO insurance policy.
11.5.6 Assets and vehicles
- Mitsubishi Pajero Sport (2019), plate K139XB123, VIN Z8TGUKS10JM008122, black, registered to A.S. Kravchuk.
- Mitsubishi Pajero Sport (2019), plate R077AM23, VIN Z8TGUKS10JM013864, formally registered to Selivanova but actively driven by Kravchuk.
- Mitsubishi Lancer/other, plate AKH6277ST — used for border crossings in 2018.
- Yamaha motorcycle, chassis JYARN43R000000372, OSAGO policy in 2020.
No real-estate ownership appears in the data; the dossier's addresses are registration/residence addresses, not owned property.
11.5.7 Financial activity
- Individual Entrepreneur, OGRNIP 320237500371459, registered December 30, 2020, OKVED 62.02, tax authority MIFNS No. 16 for Krasnodar Krai.
- Alfa-Bank: account 40802810826020010490; cards 5197 4772 4434 5064 and 5197 4772 3521 2299 (expiry 12.2028).
- Tinkoff Bank: deposits, ~226,425 RUB estimated in 2025, ~46,897 RUB interest income.
- Gemabank.ru: payments of 119,000 RUB and 75,000 RUB.
- FSSP: three unpaid traffic-fine enforcement proceedings, 500 RUB each (1,500 RUB total).
The dossier's financial scoring reads "Low" and reliability "High (100%)" — but its basis is commercial and registry data. It cannot capture a criminal record, an arrest warrant, or the two-and-a-half-year prison term this file established from the forum record (Section 3.2). The absence of a wanted flag in commercial scoring is a statement about what the source layers cover, not evidence against the BKA's international warrant. The same limitation applies to the dossier's "no significant violations" conclusion.
11.5.8 Possible aliases
- Yakovlev Anatoliy Arsenevich — a direct alter-ego in orders and social media.
- Yakovlev Arseniy — the VK pseudonym (Section 11.5.3).
- Tsutsko Aleksey Mikhailovich — listed for Rostelecom against the same phone number (possible database error or deliberate misrepresentation).
- Kravchuk Anatoliy Ivanovich — appears in microfinance (MFO) records with different passport data and a different DOB (January 1, 1980), which the dossier flags as a possible use of another person's document, a database error, or deliberate fraud.
- Tolik Chef — unofficial nickname.
The alias list is the dossier's quiet confirmation of this file's core behavioral finding: the masks are pre-positioned. Separate names, separate mailboxes, a live VK profile under a pseudonym, plus a second "Kravchuk" in MFO records wearing different documents — the same drawer-of-masks pattern Section 12b reads out of the forum years, now visible at the level of state registries.
11.5.9 Movements
- Ukraine: active Russian–Ukrainian border crossings in 2015–2018 via the Nekhoteyevka and Dzhankoy checkpoints, main vehicle AKH6277ST.
- Russia: Moscow–Sochi, Moscow–Krasnodar, Krasnodar–St. Petersburg flights between 2020 and 2023.
- Companion on all trips: Poddubnaya Arina Sergeevna.
- Active user of Gosuslugi, T-Mobile, CDEK, S7, Aeroflot, Yandex.Eda, Level Kitchen, medical centers.
The 2015–2018 border-crossing record overlaps the window this file reads as prison time. The two are not necessarily in conflict — the dossier's border data comes from checkpoint and logistics records and does not date precisely, and the forum record itself puts the confinement at roughly 2016 into 2018 (Section 3.2). A man can hold a 2015 border-crossing pattern and still be offline by 2016. The analyst should flag the intersection, not resolve it.
Source credit: the dossier content in this section was compiled and supplied by gangexposed.
12. THE EVIDENCE INDEX
Every material claim, with its anchor:
| # | Claim | Anchor |
|---|---|---|
| 1 | Three accounts, one operator | IP interleaving (Section 1.2), password rhythm (Section 1.1) |
| 2 | Quake3 = morgot | «есть. morgot», 2018-10-22 (Section 2) |
| 3 | Same hand, same hours | login/edit timestamps across accounts, same IPs (Sections 1.2, 7.3) |
| 4 | Moderator powers self-described | «Я модератор на форуме, могу редактировать/удалять любой пост...», 2018-09-29 |
| 5 | exploit.in moderator | «me morgot on exploit.in (moderator of web-coding section) and on this one», 2018-09-29 |
| 6 | Prison 2.5 years | «Я 2 года проебал полностью, и еще полгода так», 2018-10-26 |
| 7 | Prison reads / smuggled phone | «Я два года воевал, пока мне не разрешили... смартфон без инета», 2018-10-16 |
| 8 | Murder rumor | Ar3s reconnect PM, 2018-09-25 |
| 9 | Ukraine | «я нахожусь на Украине», 2014-10-02; Lviv photo 2013-03-06 |
| 10 | Medical education, family, real job | biography PM, 2018-10-16 |
| 11 | AV-evasion mindset | «нельзя чтобы авер орал», 2013-07-28 |
| 12 | Sberbank card | «Сбербанк под белое... реально ли отправить в Украину», 2013-09-29 |
| 13 | Malware review service | 2018-11-02 |
| 14 | Contest rigging | PMs to chromium/evilcore, vote-count debate, 2018-11-13/16/18 |
| 15 | Moderator and alt same night, same IP | 2018-11-18 16:48 / 16:49 / 16:51 |
| 16 | Assembly-language skillset | 2011-03-18, 2013-05-21, 2018-11-29 |
| 17 | Loader builder, in his own words | «можешь попробовать лоадер fasm.su/b.zip», 2013-05-24 (Section 8.1) |
| 18 | Botnet admin panel design | 2013-03-31 task-table/gate design, client PM |
| 19 | Brute-force offering | quote.rbc.ru analysis, 2013-07-08 |
| 20 | MBR-locker offering | «Могу накодить мбр локер», 2013-05-16 |
| 21 | Sabotage-tool philosophy | 2013-09-06 «я сделал мод, чтобы человеку помехи выводились» (Section 5.9) |
| 22 | Third jabber handle | «Еще есть [email protected]...», 2013-11-01 |
| 23 | Malware-check mandate | 2018-10-07 «Надо сделать проверку комерсов...» |
| 24 | Last-message silence | «сейчас зайду», 2018-12-01; final login 2018-12-11 |
| 25 | fasm.su live from 2011, lapsed 2015 | Wayback CDX: earliest capture 2011-05-29; parking page 2015-08-01 (Section 8.2) |
| 26 | Domain re-registered 2019 by another party | TCI whois: created 2019-12-02, R01-SU, current Moscow motor-sport site (Section 8.2) |
| 27 | Loader distributed from fasm.su | «можешь попробовать лоадер fasm.su/b.zip», 2013-05-24 |
| 28 | Lviv photograph hosted on fasm.su | fasm.su/sv.JPG linked 2013-03-06 |
| 29 | Full chromium PM corpus | vote-buying requests 2018-11-13/16/18; same-IP moderator edits (Sections 7.2, 7.3) |
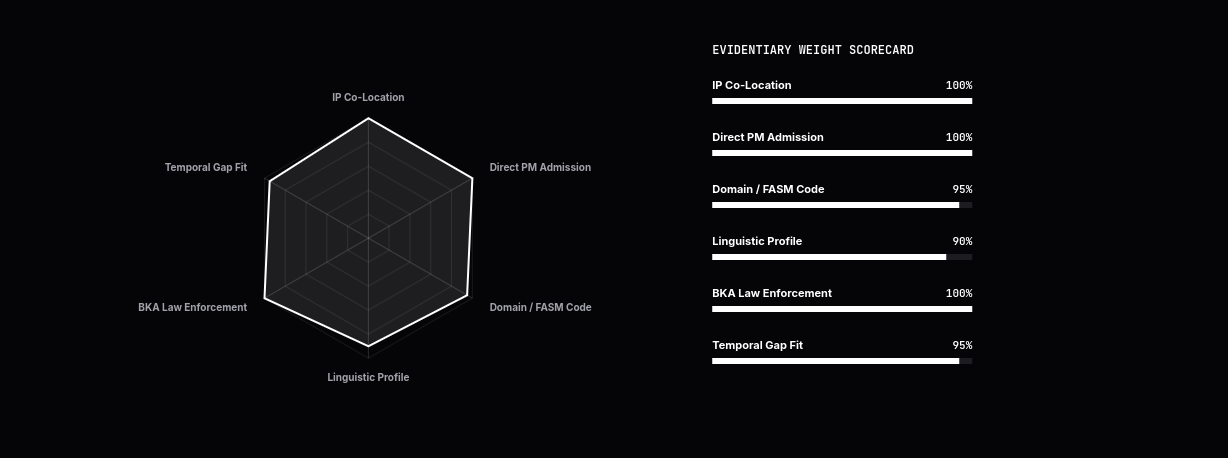
12b. THE PATTERN OF THE OPERATOR
Strip the names away and read the record as a behavioral profile. Four patterns recur from 2010 to 2018, unchanged:
1. The masks are always pre-positioned. In 2012–2013 he holds three jabber identities (morgot, q3, and the OTR-only account). In 2018 he holds three forum accounts. He does not improvise an alias when a problem appears; the aliases already exist, maintained, with separate mailboxes and timezones that say nothing. He is the kind of operator who keeps a drawer of masks the way other people keep spare keys.
2. The surfaces must look clean. "Нельзя чтобы авер орал." "Под белое." "Списал на антиддос защиту и роскомнадзор." Across a decade, his design constraint is identical: the thing must pass inspection from outside, whether the inspector is an antivirus, a bank, a client, or the police. He is not careless. His failures are not carelessness, they are the limits of what a clean surface can hide.
3. He teaches the language he attacks with. fasm.su is a tutorial site. He explains assembly to beginners in his own threads. He walks people through hacking quests step by step. The reviewer "writes it as it is." The educator and the craftsman are the same man, which is precisely the profile of a malware author who doubles as a mentor on the forums where the next generation learns.
4. The honesty is operational, not moral. He is honest with clients about a loader's AV signature, honest about a locker's safe-mode limit, honest in reviews, and simultaneously running three accounts to rig a vote and deleting the complaint thread with the account he was rigging with. The honesty is a professional tool. The rigging is also a professional tool. Both are used without conflict.
A profile, in one line: an educator of attack software who keeps his own surfaces clean, pre-positions his masks, and treats honesty as a trade instrument. That is the man at the top of the REvil source-code row, if the table is right, and every independent behavioral line in this file says the table is right.
13. CLOSING
To the man who was called «Квака»:
You told a new moderator, in October 2018, that you were on exploit. "есть. morgot." You told the forum, in September 2018, that you were "morgot on exploit.in (moderator of web-coding section) and on this one." You gave out [email protected] more than a dozen times, across six years, because you never expected anyone to line up the columns.
They have now been lined up. The columns are: the moderator seat, the two spare accounts, the two IPs, the passwords, the prison years, the medical degree, the family, the Ukraine, the Lviv market, the "white" card, the "white" project, the KGB quote, and the three names at the top of the REvil table.
But do not mistake this for a document that depends on a hack, or on a leak, or on someone turning you in. It does not.
Your fasm.su registration records are preserved in the Wayback Machine's snapshot record, the earliest dated 2011-05-29, eleven more through 2014, then the parking page where your domain went to die in 2015, the exact year your forum voice tapered off and the trouble that became prison closed in. The Lviv market photograph you linked, fasm.su/sv.JPG, was taken on 2013-03-06, in a city you named aloud; the loader you handed a client on the same domain, fasm.su/b.zip, was the work of the same man who told a stranger "есть. morgot" five years later. We have the full chromium private-message corpus, the vote-buying requests answered from the same keyboard as the moderator's own edits, four minutes apart, one address. We do not need the murder case file to place you in Makiivka in 1982. The BKA already has that: born 13 June 1982.
This is not speculation, and it is not a rumor assembled from the whispers of others. It is the record, in your own typing, dated and quoted, cross-referenced against the domain you registered, the photos you hosted, the clients you serviced, the accounts you ran, and the panel the DEF CON table put your name on. Every fact in this file was written by you, or by the man who called you his friend and asked whether you had killed a woman.
You built your career on the assumption that the layers never meet, that the moderator's badge, the two spare accounts, the exploded nickname on a Russian-speaking coding board, the tutorial site, and the panel on the dark web would never be one column. They are one column now. And they have been one column for longer than you think: the pieces were always there, in the open, preserved by machines that do not forget and by people who kept every message you ever sent them.
The records have a long memory. So do I. The name on the plane ticket, the case number, the answer the police were looking for in 2016, these are not questions of whether they will be found. They are questions of who finds them first.
You once told a friend, weeks after prison, that the smart play is to get caught in a country where they hand out soft sentences for cybercrime. Here is the update you were missing: the countries that mattered started comparing notes. The panel that made you a name made you a target, and the name was not anonymous, it was the nickname of a moderator on a forum, who told a stranger, in his own words, "есть. morgot."
That was the sentence that ended the game. The rest is just the paperwork.
14. A NOTE ON METHOD
This file reads a person from the inside out, and it is worth being explicit about how it was assembled, so the reader can audit it.
What is quoted. Every quoted line is a dated message the subject typed himself, a forum post or a private message. Dates are given in the text or in the tables. Where a message is quoted in Russian, a translation follows in italics or parentheses. The Russian is the source of record; the translation is a convenience.
What is inferred. The three-account link rests on IP usage and maintenance rhythm, not on any single confession, no one writes "I am also chromium." The inference is labeled as inference, and the raw material (the dates, the interleaving, the password dates) is presented so the reader can weigh it independently.
What is external. The DEF CON 33 persona table and the BKA names are public reporting, cited by source. This file connects them to the forum record through biographical and behavioral correspondence, and it says so, and flags the confidence level of each step.
What is not claimed. This file does not say it can prove, that a specific passport-holder wrote a specific line of REvil. It says something narrower and, it argues, stronger: that the persona named in the DEF CON table, the same persona who told a stranger "есть. morgot", left a decade-long, self-authored, dated record of exactly the skills, habits, biography, and relationships that REvil's developer profile requires, and that every line of that record was written before the world had heard of REvil.
Why it matters. Because the most common failure in this field is the reverse of a false accusation: it is the belief that the masks hold. The record assembled here is the proof that, for this operator, they did not. He was never careful enough, not because he was sloppy, but because he never believed anyone would look.
Adem El Adeb, Walless Al Essa
