The Rise and Fall of Doxbin
"KT" (AKA "Kayte" and doxer on Telegram) is the foundational admin and co-founder of the clearnet version of Doxbin.
Not to be confused with Doxbin Darknet, a pastebin initially launched on the Tor network in May 14, 2012 by "Nachash" before being seized by international law enforcement during Operation Onymous in November of 2014. The modern clearnet incarnation was established in early 2018 by KT alongside a partner by the handle of "Brenton".
Together, they built the site as a pastebin dedicated exclusively to publishing PII (Personally Identifiable Information) to facilitate intimidation, harassment, extortion and swatting attacks (much like Doxbin Darknet).
Under KT's administration, Doxbin grew from an obscure repository into a monumental platform for the cybercrime ecosystem; SIM Swapping groups and harassment collectives, known colloquially as the "The Com", padded the ranks of the site.
KT and Brenton monetized the site via a coercive blacklist system under which victims whose private information was posted on the website were forced to pay the admins, typically in Bitcoin, to have their files removed or permanently barred from re-upload.
In January 2022, backend database records from Doxbin were breached, revealing account details of the platform's founders:
| User ID | Username | Primary Contact / Email | Role & Hierarchy | Operational Function |
|---|---|---|---|---|
| 1 | kt | [email protected] / @doxer | Founding Administrator / Owner | Platform maintenance, dispute resolution, doxing |
| 2 | Brenton | [email protected] / t.me/brenton | Founding Co-Owner | Co-administration, backend operations |
| N/A | White | t.me/whitedoxbin | Interim Owner (Late 2021–Jan 2022) | Purchased site; subsequently ousted and doxed |
| N/A | Operator | @DrivenTowards2 | Successor Owner (June 2023) | Assumed control following KT's departure |
| N/A | River | Alleged Romanian national | Subsequent Administrator (2024–2025) | Operated site prior to the February 2025 compromise |
In November of 2021, KT negotiated the sale of doxbin for $75,000 to an actor under the alias "White" (Later revealed to be a British teenager called "Arion Kurtaj", the co-owner of the hacking team known as Lapsus)
Due to Kurtaj's technical dysfunction, frequent site outages and instability which inticed hostility across the platform's user base, and with sustained community harassment, in January 2022, Kurtaj agreed to sell Doxbin back to KT and Brenton at an estimated 80% financial loss, and just before giving up administrative control, Kurtaj publicly released Doxbin's core database on Telegram, exposing over 370,000 user profiles, 700,000 associated emails, hashed passwords, session logs, user-agent details and so on.
This breach triggered retaliation from KT, which caused him to publish an exhaustive dox of Kurtaj. The exposure compromised Kurtaj's operational security, allowing investigators and the City of London Police to locate, raid, and apprehend him in the spring of 2022 in connection with Lapsus intrusions into NVIDIA, Rockstar Games, and Microsoft.
Two Men, One Moniker
On the 14th of July, 2026, an article released by the BBC and the Crown Prosecution Service announced that a Welsh man, Callum Dare (26, from Talbot Green in Rhondda Cynon Taf), had been arrested on October 2019 because of his involvement with bomb threats and violent swatting.
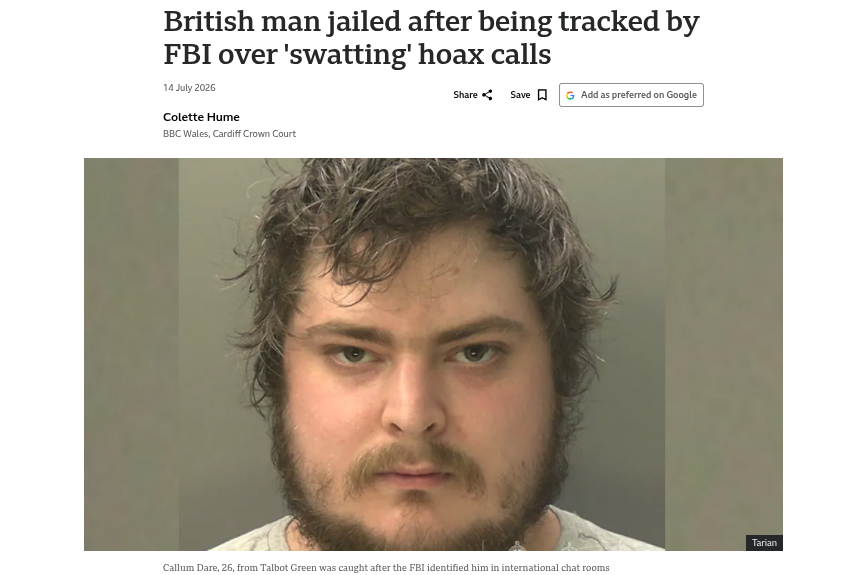
The investigation originated in May 2019 after the FBI alerted South Wales Police and Tarian, the Regional Organised Crime Unit for southern Wales, regarding transnational swatting incidents targeting individuals and institutions across the United States and Canada; federal agents traced these activities to Doxbin and an associated dark-web IRC channel designated #deadnet, where users exchanged stolen identities and coordinated hoaxes.
Forensic analysis of the network's administrative logs showed that an individual using the monikers "KT" and "Chans" managed the community, facilitated doxing, and claimed responsibility for orchestrating armed police raids.
Investigators identified Dare by tracing server infrastructure subscriptions, payment processors, trails, and email records back to his PayPal account and home address in Talbot Green.
Despite Callum Dare's conviction establishing his role as "KT" and "Chans" during the early period of Doxbin and "#deadnet", subsequent legal filings by the USA DOJ and investigative reporting indicate that the "KT" moniker was also used by a separate actor in Australia
In March 2023, the U.S. Attorney's Office for the Eastern District of NY unsealed criminal charges against Nicolas Ceraolo ("Convict") and Sagar Steven Singh ("Weep") for computer-intrusion offenses tied to syndicate named "ViLe": federal charging documents identified the Doxbin admin who worked alongside ViLe as an unindicted co-conspirator designated "CC-1"
Public reporting on 2024 by Brian Krebs established that CC-1 utilized the handles "KT" and "Kayte"
| Analytical Dimension | The Welsh Entity (Callum Dare) | The Australian Entity ("CC-1" / "Kayte") |
|---|---|---|
| Legal Identity | Callum Dare (Born Jan 30, 2000) | Unnamed 23-year-old male in DOJ filings |
| Geographic Base | Talbot Green, Rhondda Cynon Taf, Wales, UK | Coffs Harbour, New South Wales, Australia |
| Judicial Disposition | Arrested 2019; Convicted Cardiff Crown Court | Identified as unindicted co-conspirator CC-1 |
| Operational Focus | #deadnet IRC, SiegeCulture, swatting networks | ViLE group, DEA breach, clearnet platform monetization |
| Primary Handles | "KT", "Chans" | "KT", "Kayte", Telegram: @doxer |
The Investigation Begins
Two distinct "KT"'s would make anyone curious, especially us. This is why VULONE decided to launch an in-depth investigation on the original KT: the Doxbin admin, the ViLE facilitator, the person behind it all.
We started by looking up "KT" on VULONE:
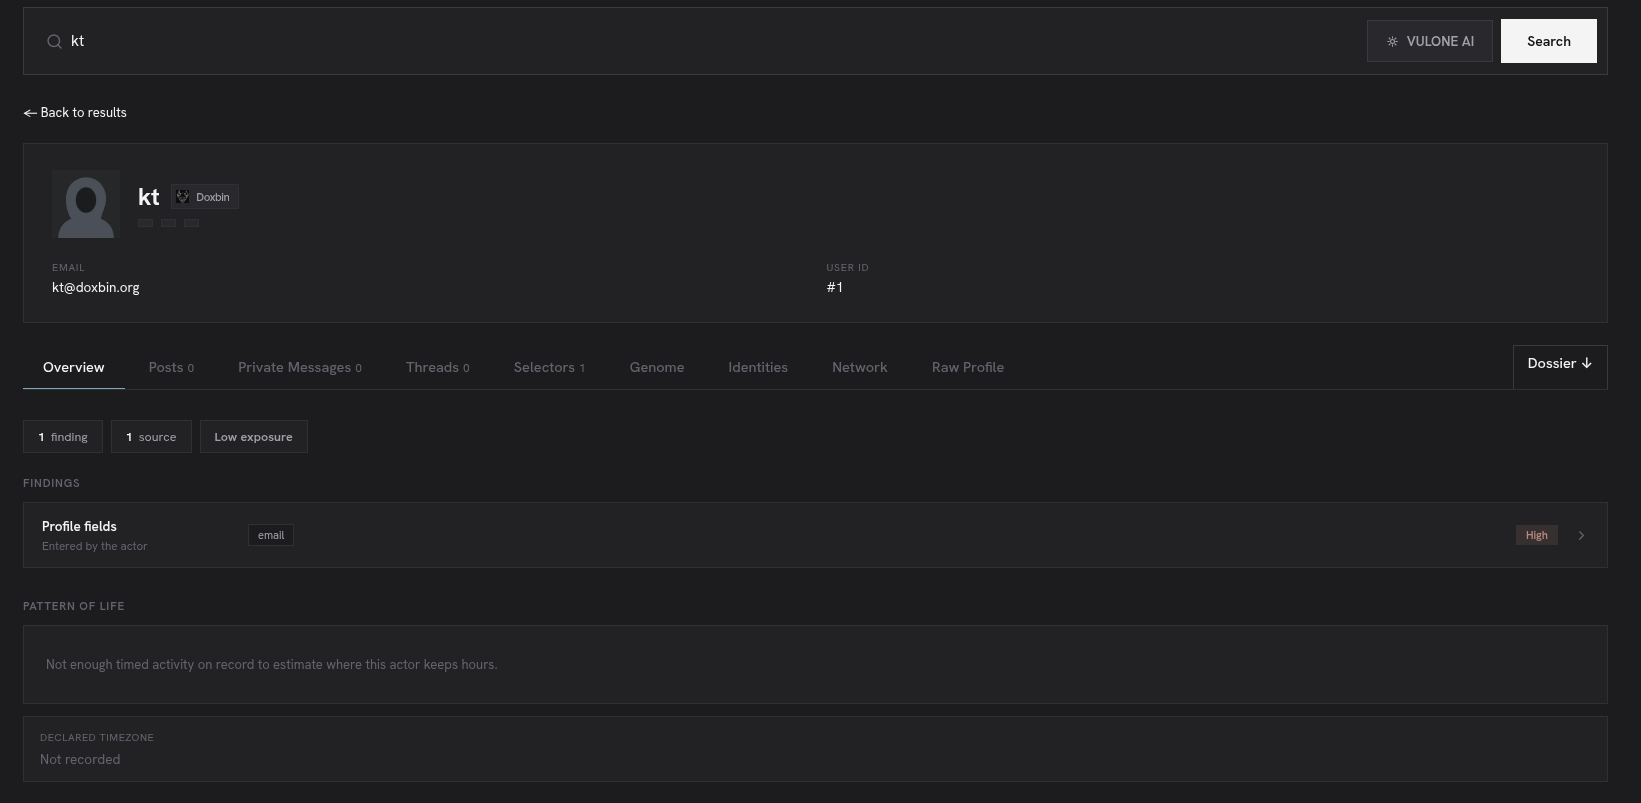
Looking up KT only yields a Doxbin profile with an email that gave little to work with, but we didn't stop there; trying permutations of his common handles, we managed to find multiple hits on the username "Katy".
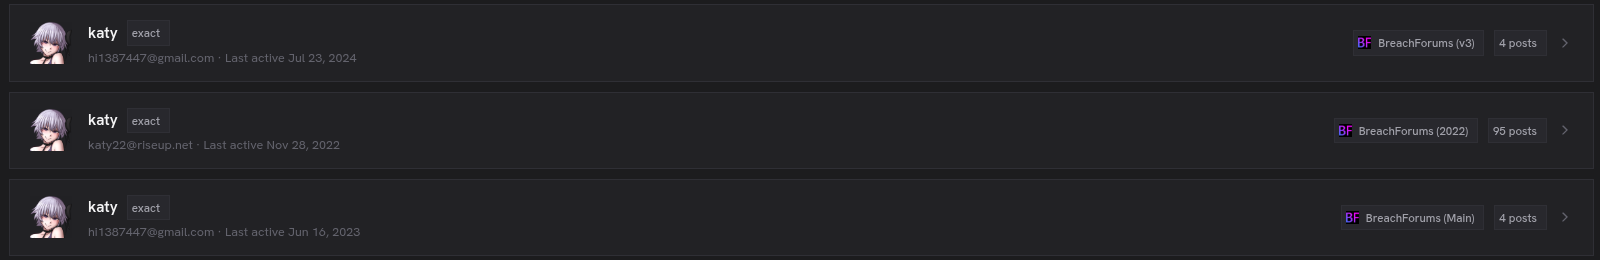
Most interesting was the Breachforums profile: it had 95 posts on record along with 116 private messages:
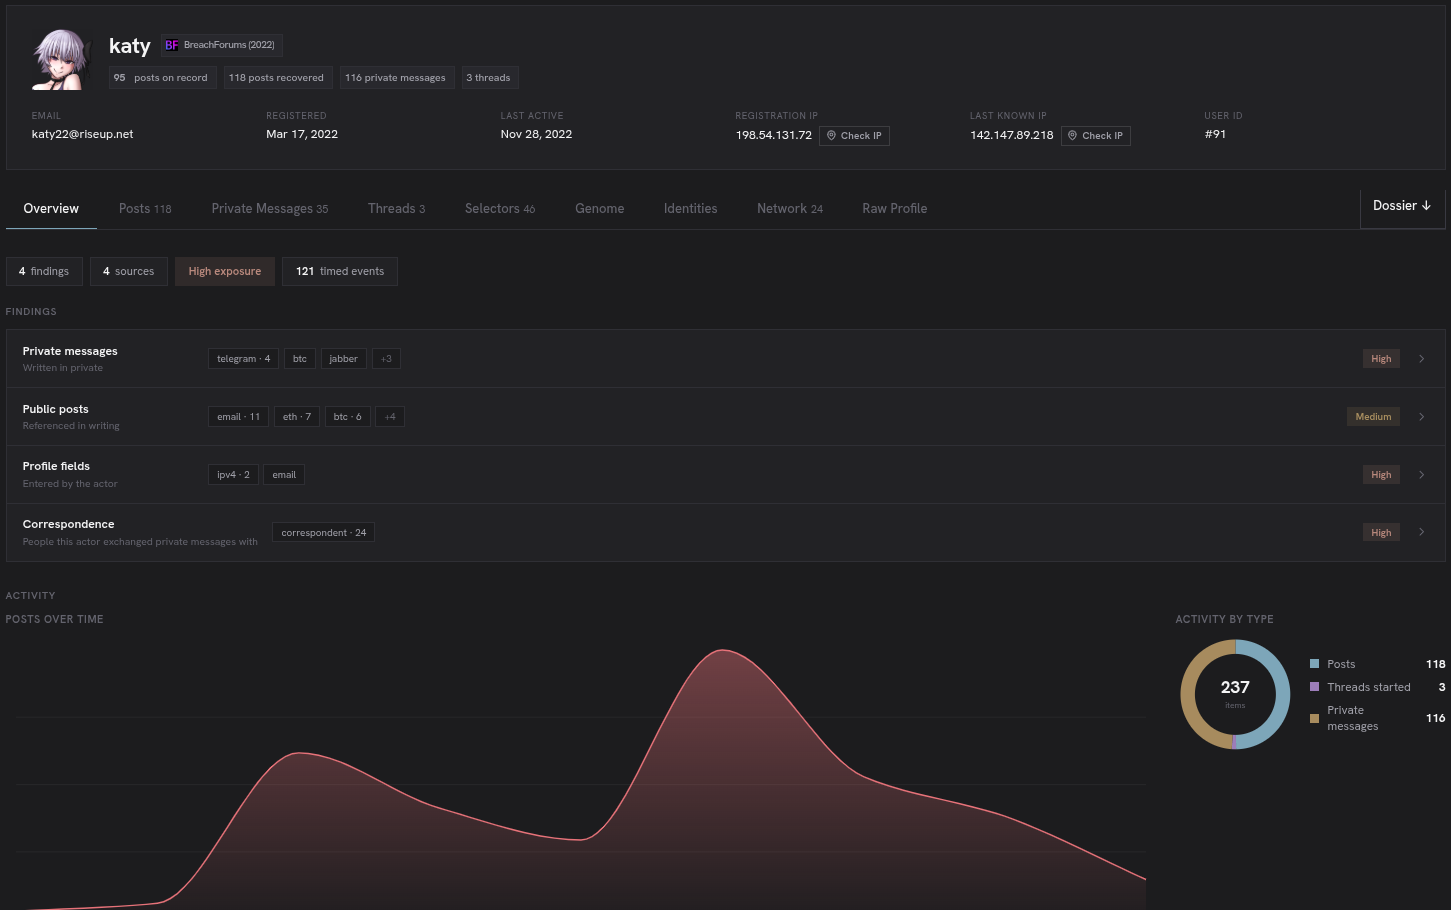
Same username on Breachforums used multiple emails including:
With multiple IP logs:
103.75.11.62173.231.215.101198.54.131.72142.147.89.218
Interesting. Interesting as to where we kept looking.
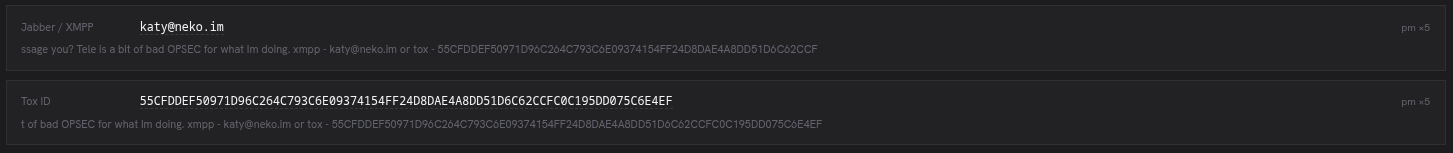
- Jabber: [email protected]
- Tox: 55CFDDEF50971D96C264C793C6E09374154FF24D8DAE4A8DD51D6C62CCFC0C195DD 075C6E4EF
- Telegram: @doxer | This is important since it links this profile with our KT.
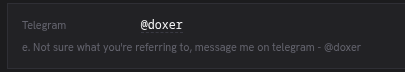
What's more interesting, and arguably the most grave mistake, is what we find when sifting through his private messages on the forum:
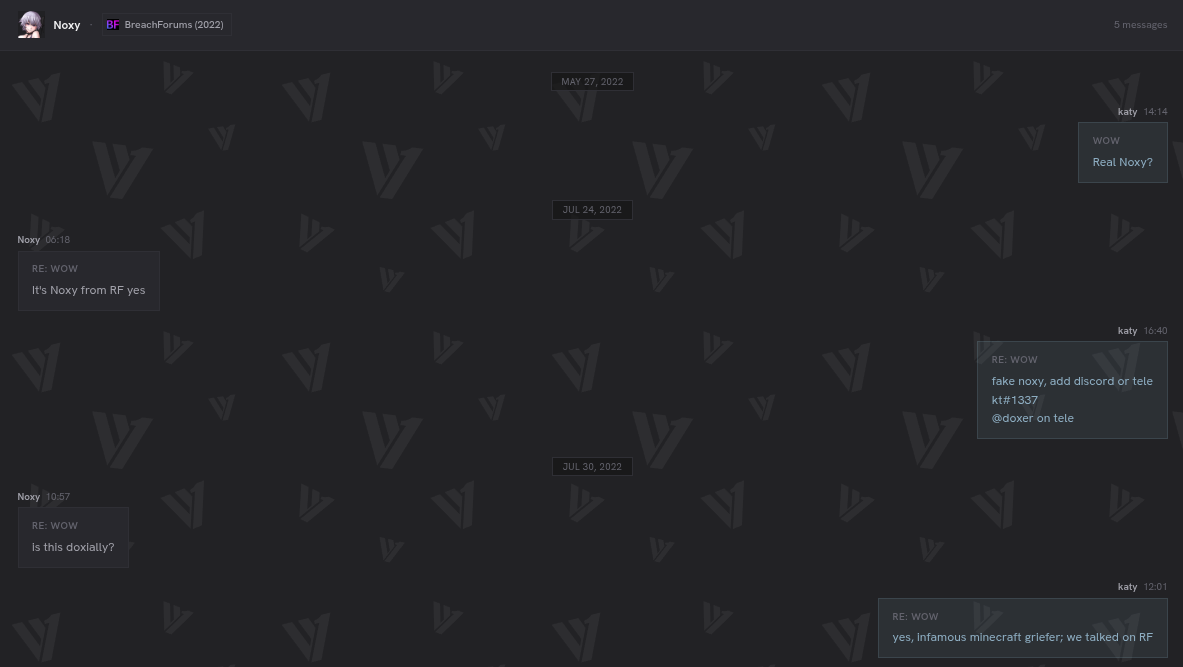
In an interaction with an apparent old friend under the alias "Noxy", Noxy questioned Kayt's identity and asked if he's "Doxially", a Minecraft griefer (a griefer is one who, with or without cheating, intentionally causes destruction on multiplayer Minecraft servers), in which KT replied with Yes, confirming it.
Nice! A new pivot point in the investigation with a possibly less-skilled KT of the past we could dig through.
All Roads Lead To Minecraft
With any other threat actor that began his career on Minecraft, KT is not an exception. Looking up Doxially on Google gives us a Youtube channel of an "infamous" Minecraft griefer, that made a name for himself by griefing and exploiting on numerous Minecraft servers such as Mineplex, HiveMC, and others.
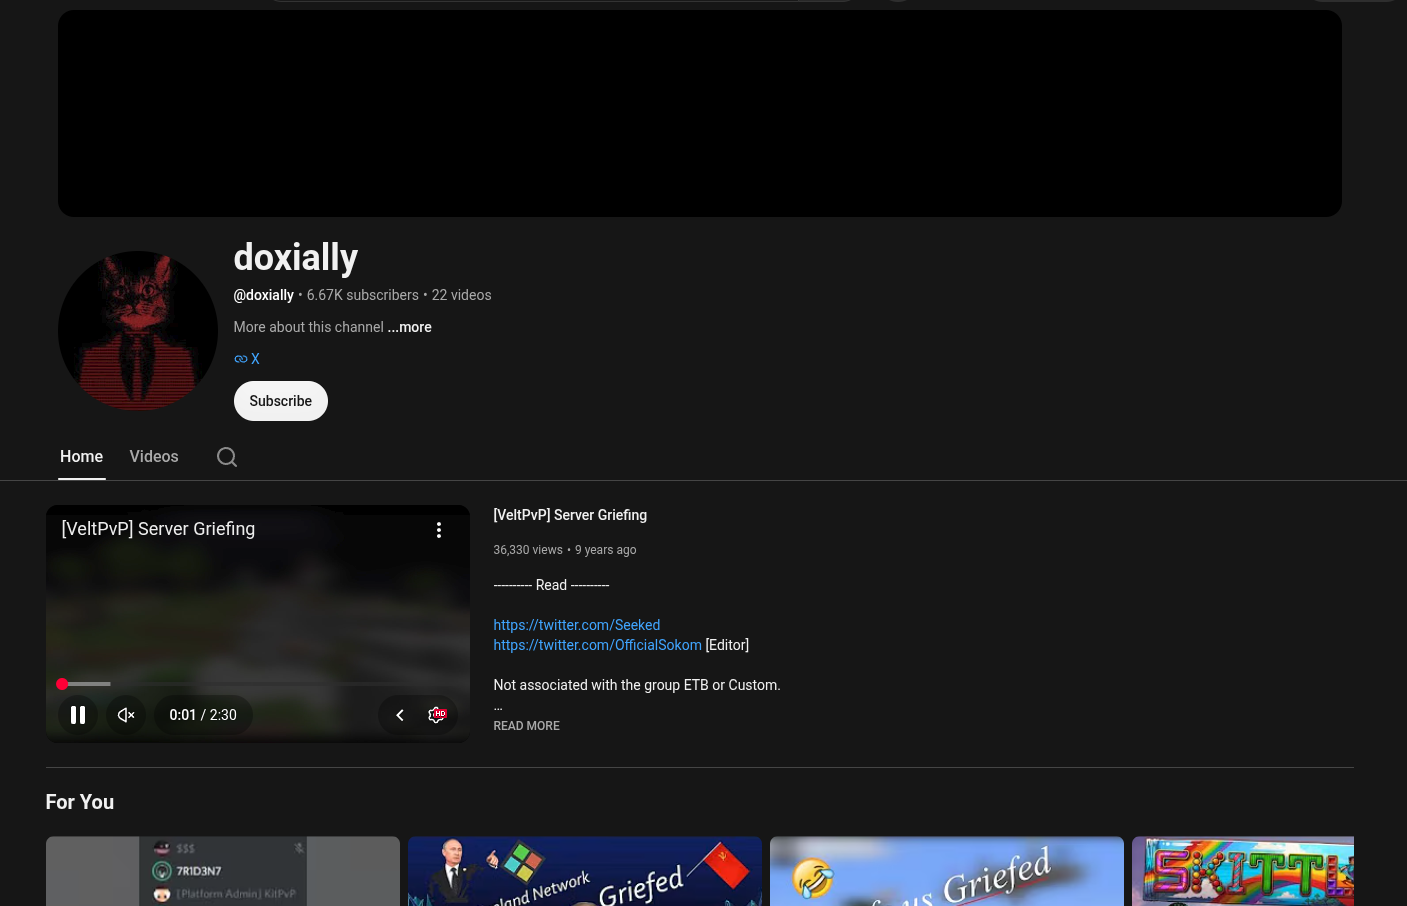
Sifting through Doxially's youtube videos, we manage to find a video where he's taunting Mineplex moderators with a compromised admin account, in which he uses to send a message:
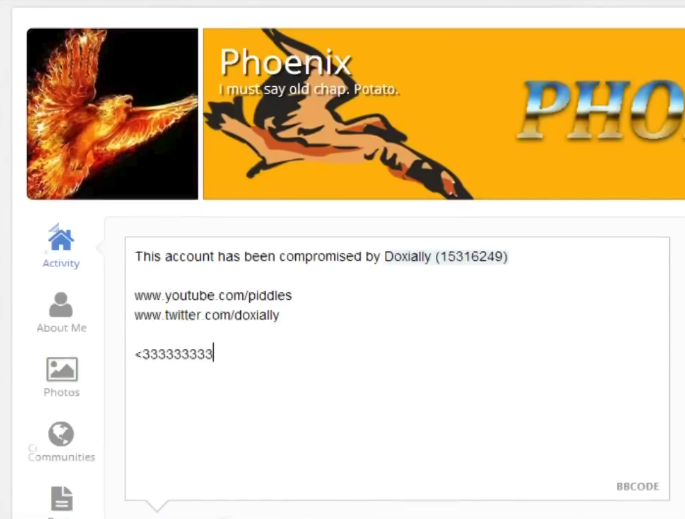
What's interesting about this message is that it says youtube.com/piddles instead of youtube.com/doxially; we first suspected it to be an old channel, but visiting the Piddles channel, it appears to be an even older channel than Doxially's. We can presume that "Piddles" was just the old link for "Doxially," and after he changed the link, another individual simply just claimed it.
We can see him boast about it again on another video!
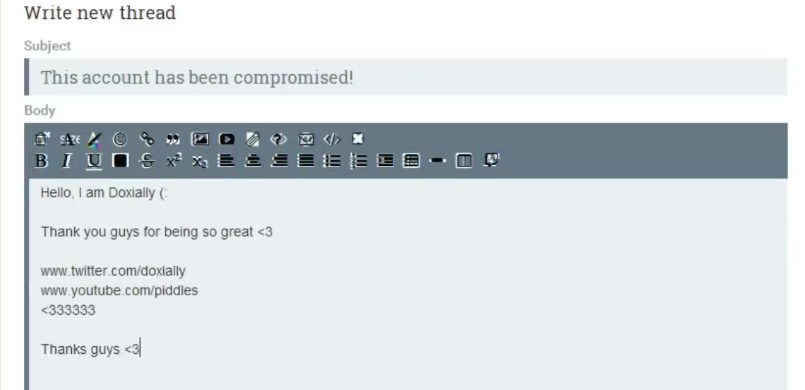
We can note now that the usernames Doxially and Piddles belong to KT.
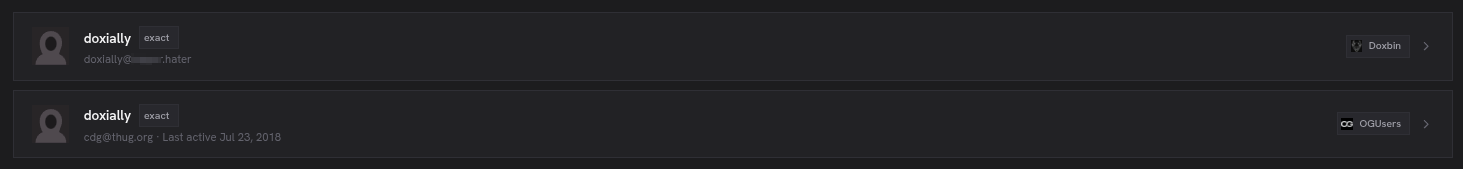
Looking up Doxially on VULONE gives us 2 profiles, one on Doxbin, one on OGUsers, all which seem to use throwaway emails, profiles are mostly empty.
However, looking up Piddles gives us a very interesting find.
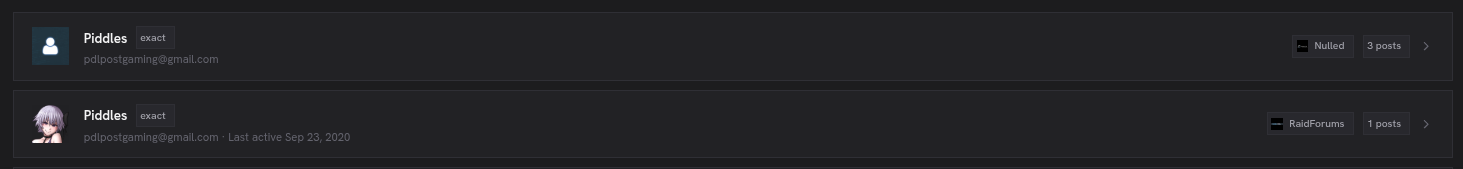
Piddles / Doxially, the Minecraft griefer, had a Nulled and RaidForums accounts. Accounts registered with the same email, "[email protected]".
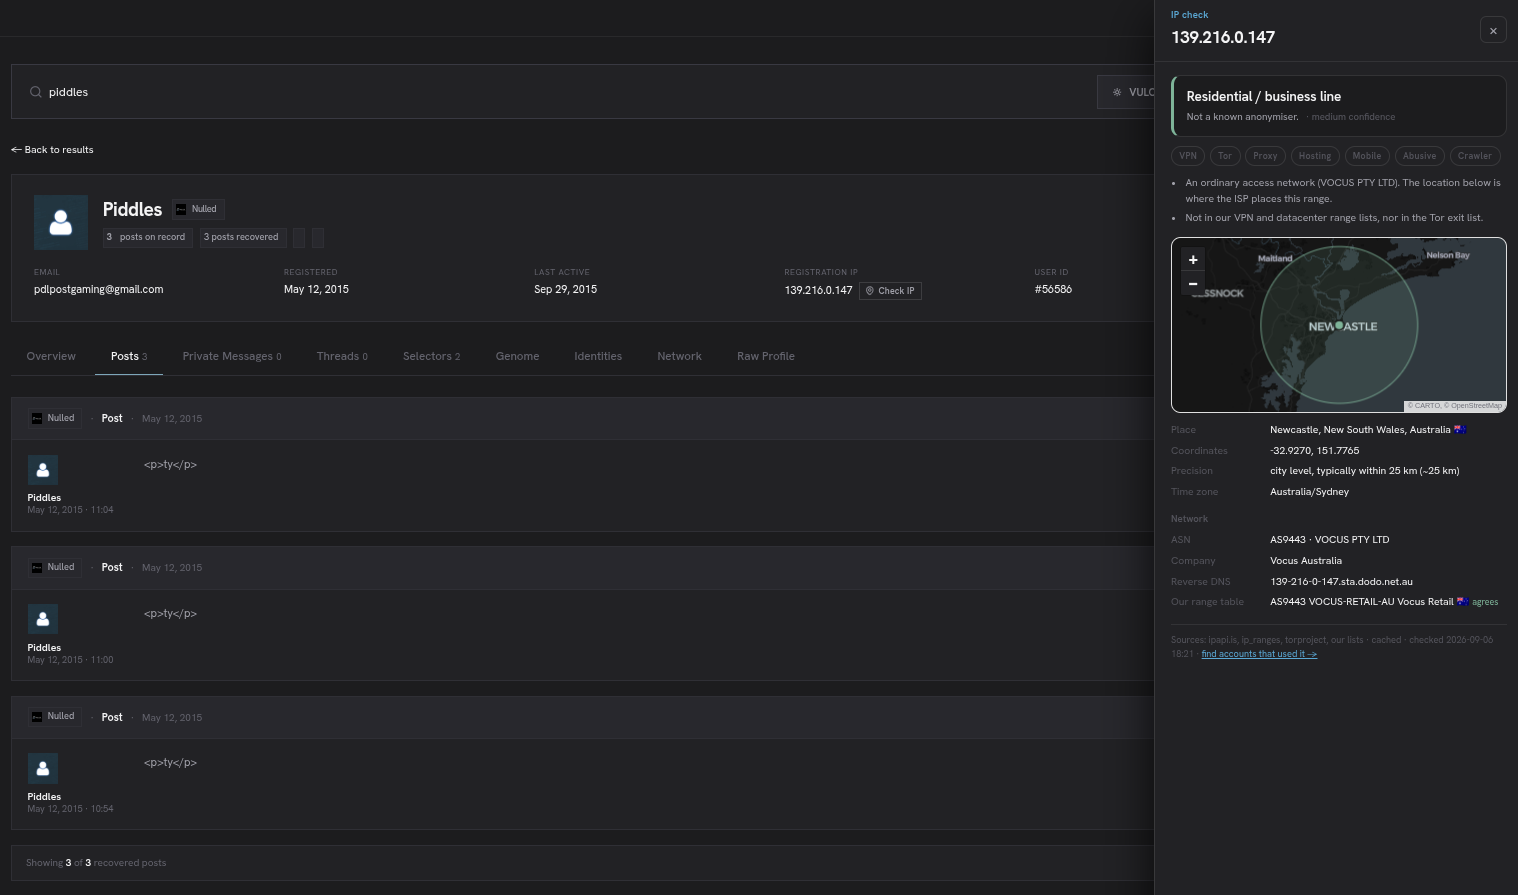
BINGO! Clicking on Piddles's Nulled account and Geo-locating the IP gives us Australia, the same country AND state CC-1 / KT is from according to DOJ filings and Brian Krebs (New South Wales, Australia).
So recap, we've confirmed KT / CC-1 / Kayt, the Doxbin administrator, to be Doxially / Piddles, a Minecraft griefer from South Wales, Australia.
One Email, Many Breaches
Now let's dive deeper into the email [email protected], using a quick HIBP lookup
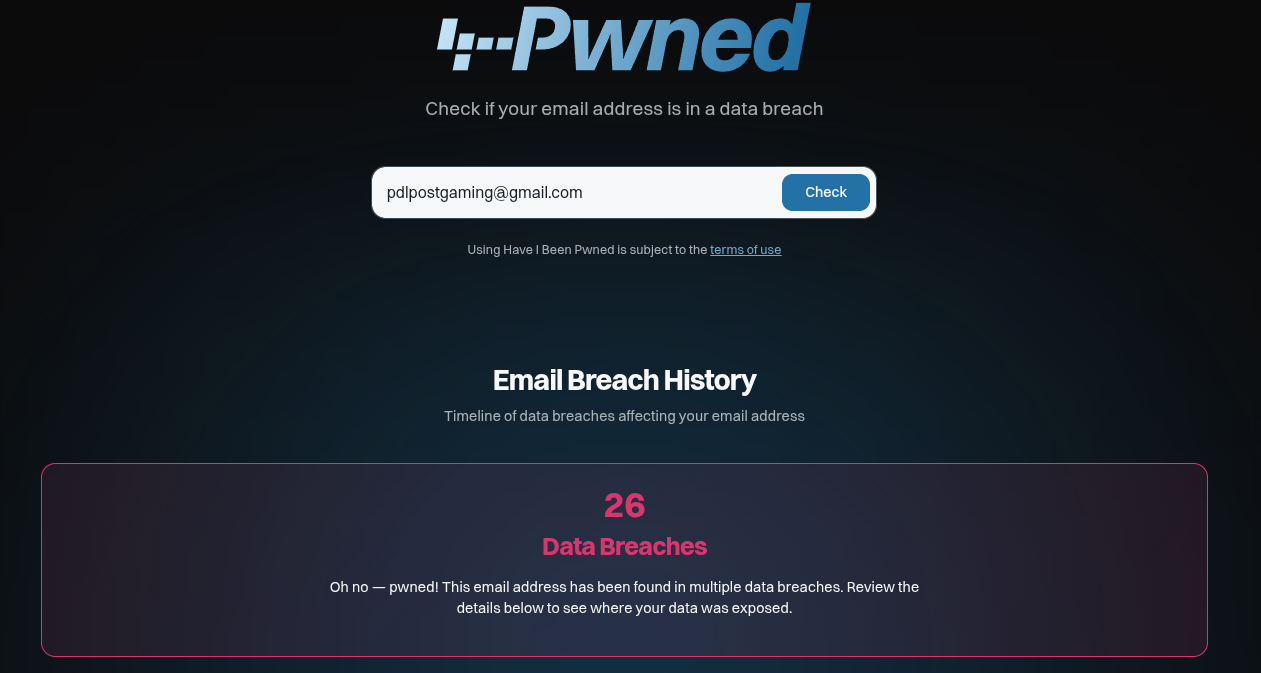
We determine that this email has witnesses multiple data-breaches, here are some we were able to recover:
| Source | Record Details |
|---|---|
| lizardstresser.su | • ID: 125202• Username: Piddles• Password: lollypop@123• Email: [email protected]• Rank: 0• Membership: 0• Expire: 0• Status: 0• Used: 0• Domain: gmail.com |
| MinecraftStresser | • Username: pdlpost• Email: [email protected]• IP: 139.216.0.147 |
| OGU | • UID: 6614• Username: katy• Email: [email protected]• IP: 81.171.108.174, 81.171.108.176• Domain: gmail.com |
| weleakinfo.com (Record 1) | • Email: [email protected]• Created (UTC): 2019-12-03 11:33• Card Info: Visa Debit *3001 (Exp: 2/2022, Issuer: AU, Fingerprint: n2OLCplWt0cNXz3O)• Cardholder Name: Katy• Billing Address: 20 Mimiwali Dr, Bonville, NSW 2450, AU |
| weleakinfo.com (Record 2) | • Email: [email protected]• Created (UTC): 2019-09-19 06:30• Card Info: Visa Debit *3001 (Exp: 2/2022, Issuer: AU, Fingerprint: n2OLCplWt0cNXz3O)• Cardholder Name: Dox• Billing Address: 91 Forge Street, Sydney, NSW 2001, AU |
| raidforums.com | • UID: 121318002• Username: Piddles• Salt: gcoKfDUt• Email: [email protected]• Domain: gmail.com |
These data-breaches give us a very good insight on who this email belongs to, first the undeniable proof that this email belongs to KT, with the Cardholder name being "Katy" and "Dox" on the 2 records from Weleakinfo.com.
And the fact that the IPs, and the addresses are all in NSW, AU.
Unmasking KT
Running an Osint Industries scan on the email, yields the following results:
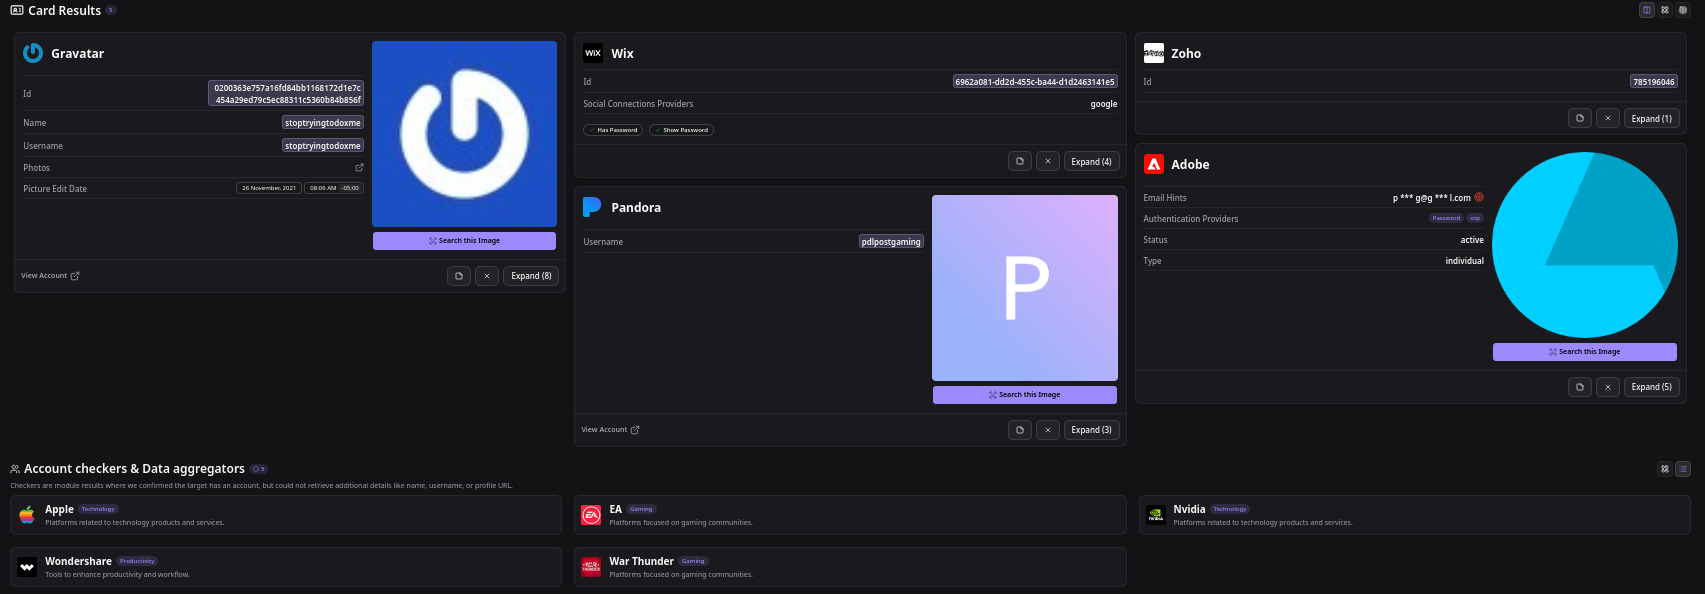
KT seems to be taunting people who got this far by making his username "stoptryingtodoxme". (Sorry, but no.)
Digging deeper, we find the email to be associated with a GitHub account called "Doctr1".
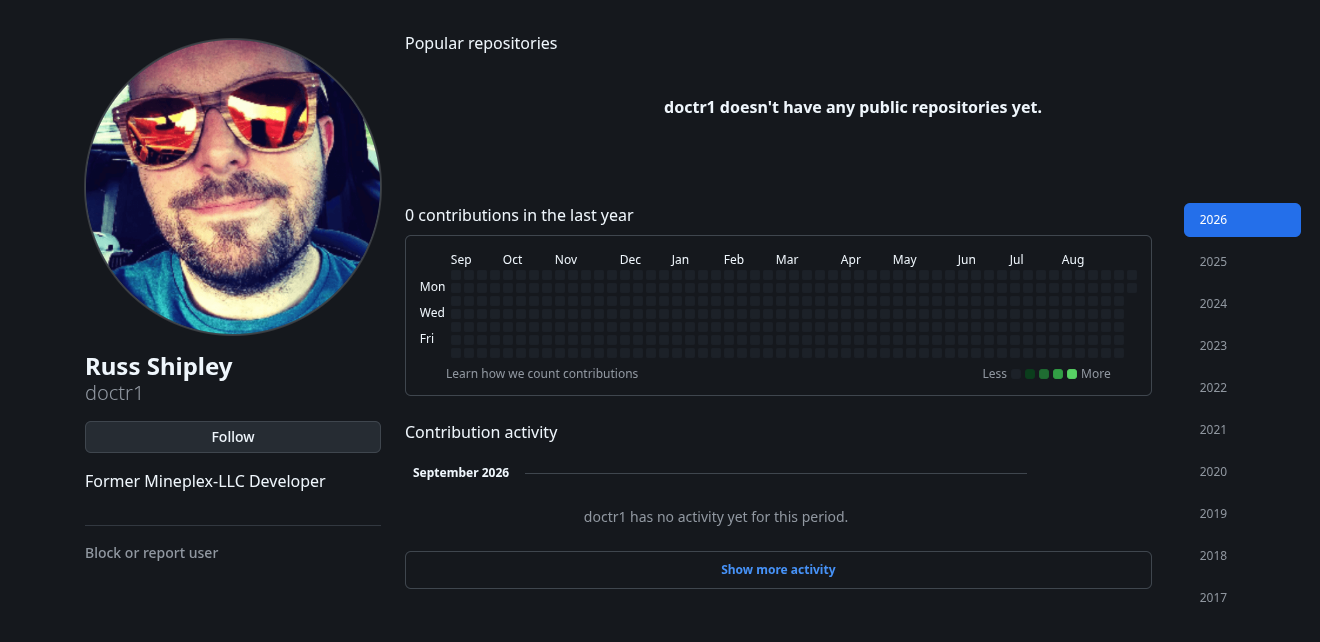
Display name says "Russ Shipley" a self-proclaimed former Mineplex-LLC developer, could this be our guy?
The profile picture seemed unique, a quick lookup using Yandex proves the picture's uniqueness:
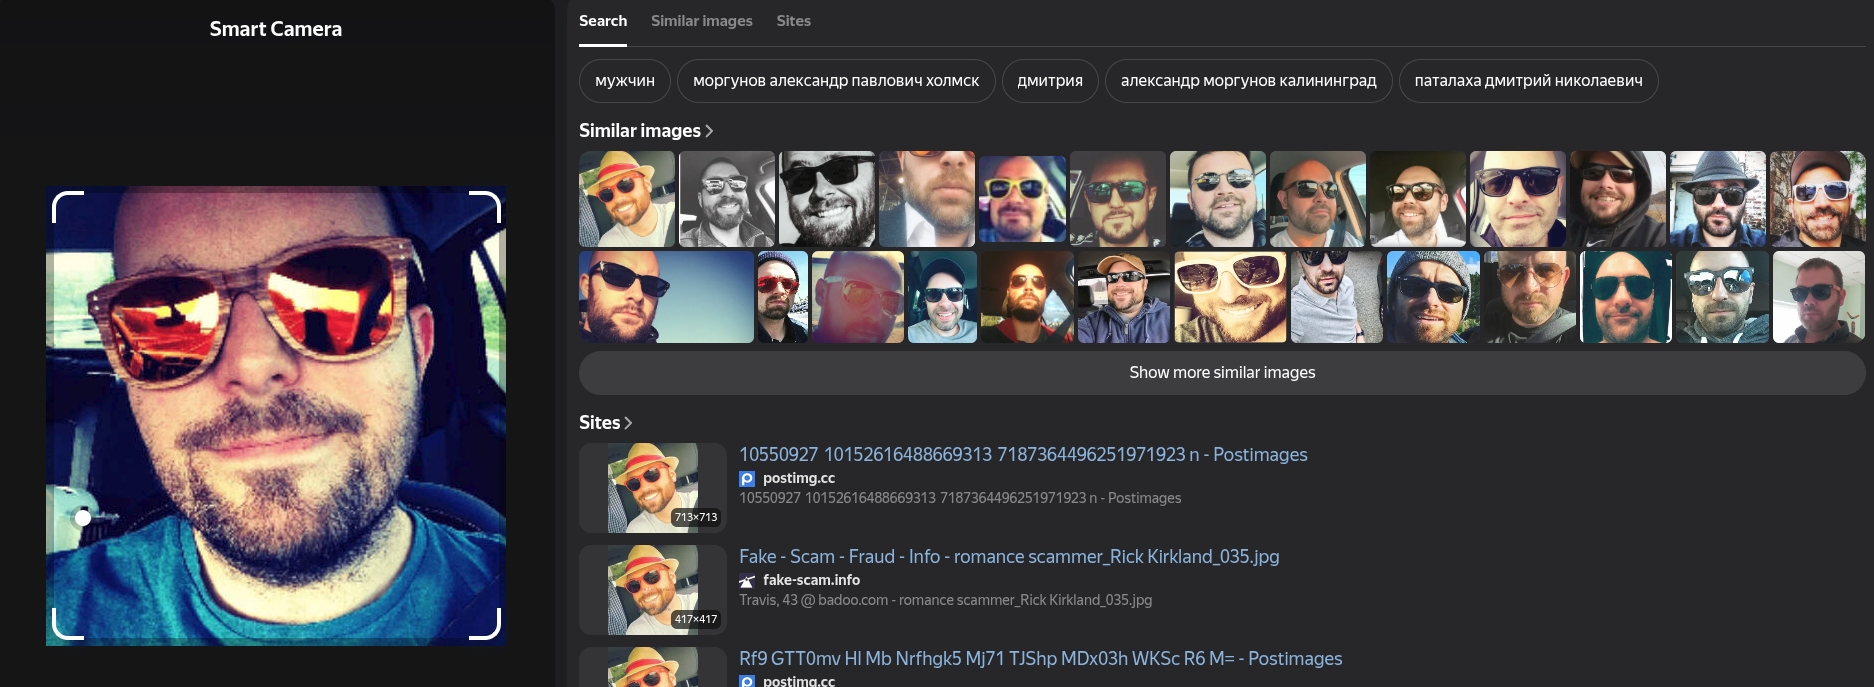
Initially we thought this might be a detrace, especially with the taunt on his Gravatar, we dismissed it but we kept it in mind.
Going further, we chose to simply throw everything out. We used Google Dorking to find any links to this peculiar alias we discovered: PDLPost. Sure enough, we felt a tug on the hook.
| Data Point | Link |
|---|---|
[email protected] | Correlated via 'pdlpost'—a username registered on Breachforums. |
[email protected] | Evident. Recovered via wildcarding. (1) |
[email protected] | [1] |
[email protected] | [1] |
[email protected] | [1] |
[email protected] | [1] |
[email protected] | [1] |
Pay attention to that last one, as tpg.com.au was actually breached! Naturally, PDLPost was in this breach. Not just [email protected], though. But a few more emails with PDLPost in them... Namely, [email protected], registered under the name Priscilla Shipley and under Kevin Shipley, which we assume are parents.
The Gravatar taunt telling investigators to "stoptryingtodoxme" wasn't a masterclass in counter-intelligence after all, the GitHhub was also not a a decoy designed to lead us astray.
It was simply arrogance. For half a decade, the moniker "KT" cast a heavy shadow over the clear-net, operating and up-keeping a ruthless ecosystem of extortion, armed swatting raids, SIM-Swappers, and ruined-lives, all hiding behind layers of proxies, dark-web infrastructure, and recently a mistaken identity of a Welsh criminal.
At last, the kingpin behind the internet's most weaponized doxing archive wasn't dismantled by federal wiretaps or high-level 0-days. He was undone by his own childhood footprints, a string of Minecraft griefing videos, a forgotten payment on a booter service, and his real surname sitting plain as day on a public developer profile, certainly not a bad way to look for work, but it's certainly not a great OpSec practice,
So hello, KT. Hello, Russ Shipley.
