


Incident Response & DFIR
Resolve the handle, wallet, or contact behind an intrusion to the operator running it, across forums, with evidence, mid-investigation.
Ransomware threat intelligence that tracks the actors, infrastructure, and attribution behind who's targeting you.
Intelligence drawn from across the global threat landscape
VULONE tracks ransomware groups across their full lifecycle, from the forums they recruit on to the infrastructure they burn.
Leak sites, forums, and infrastructure monitored continuously. Signals captured as they appear, not compiled after the fact.
The feed never stops.Aliases, tooling, and infrastructure matched across operations. When a crew rebrands, the profile follows them.
A new name is not a new group.Every claim carries its source, its date, and a confidence rating. Assessed, corroborated, and unverified are labeled as such.
Evidence you can defend.Living records of every tracked operation. TTPs mapped to ATT&CK, infrastructure indicators, victimology, and lineage.
Not frozen at publish date.New victim posts, resurfacing groups, fresh recruitment. You hear about movement when it happens.
Minutes, not weeks.Continuous watch for your organization in group chatter and staging activity, before the leak goes public.
The window before impact.Resolve the handle, wallet, or contact behind an intrusion to the operator running it, across forums, with evidence, mid-investigation.
Trace a wallet back to the actor who advertised it, and surface every alias and identifier tied to them across underground communities.
Turn cross-forum attribution into a sourced, timestamped, defensible dossier, every link backed by evidence, exportable for a case.
Pivot on any identifier and map an actor's presence across boards and time, without six open tabs and manual guesswork.
Forum accounts and personas from the underground communities, merged where the evidence ties them together.
Emails, IPs, ICQ, Skype, Telegram and Jabber handles, onion addresses, crypto wallets, Tox and PGP keys, each tied to the actor who used it.
Every row of the indexed underground communities: forum posts, private messages, member profiles and activity logs.
Cyber Investigations
Oct 31, 2026
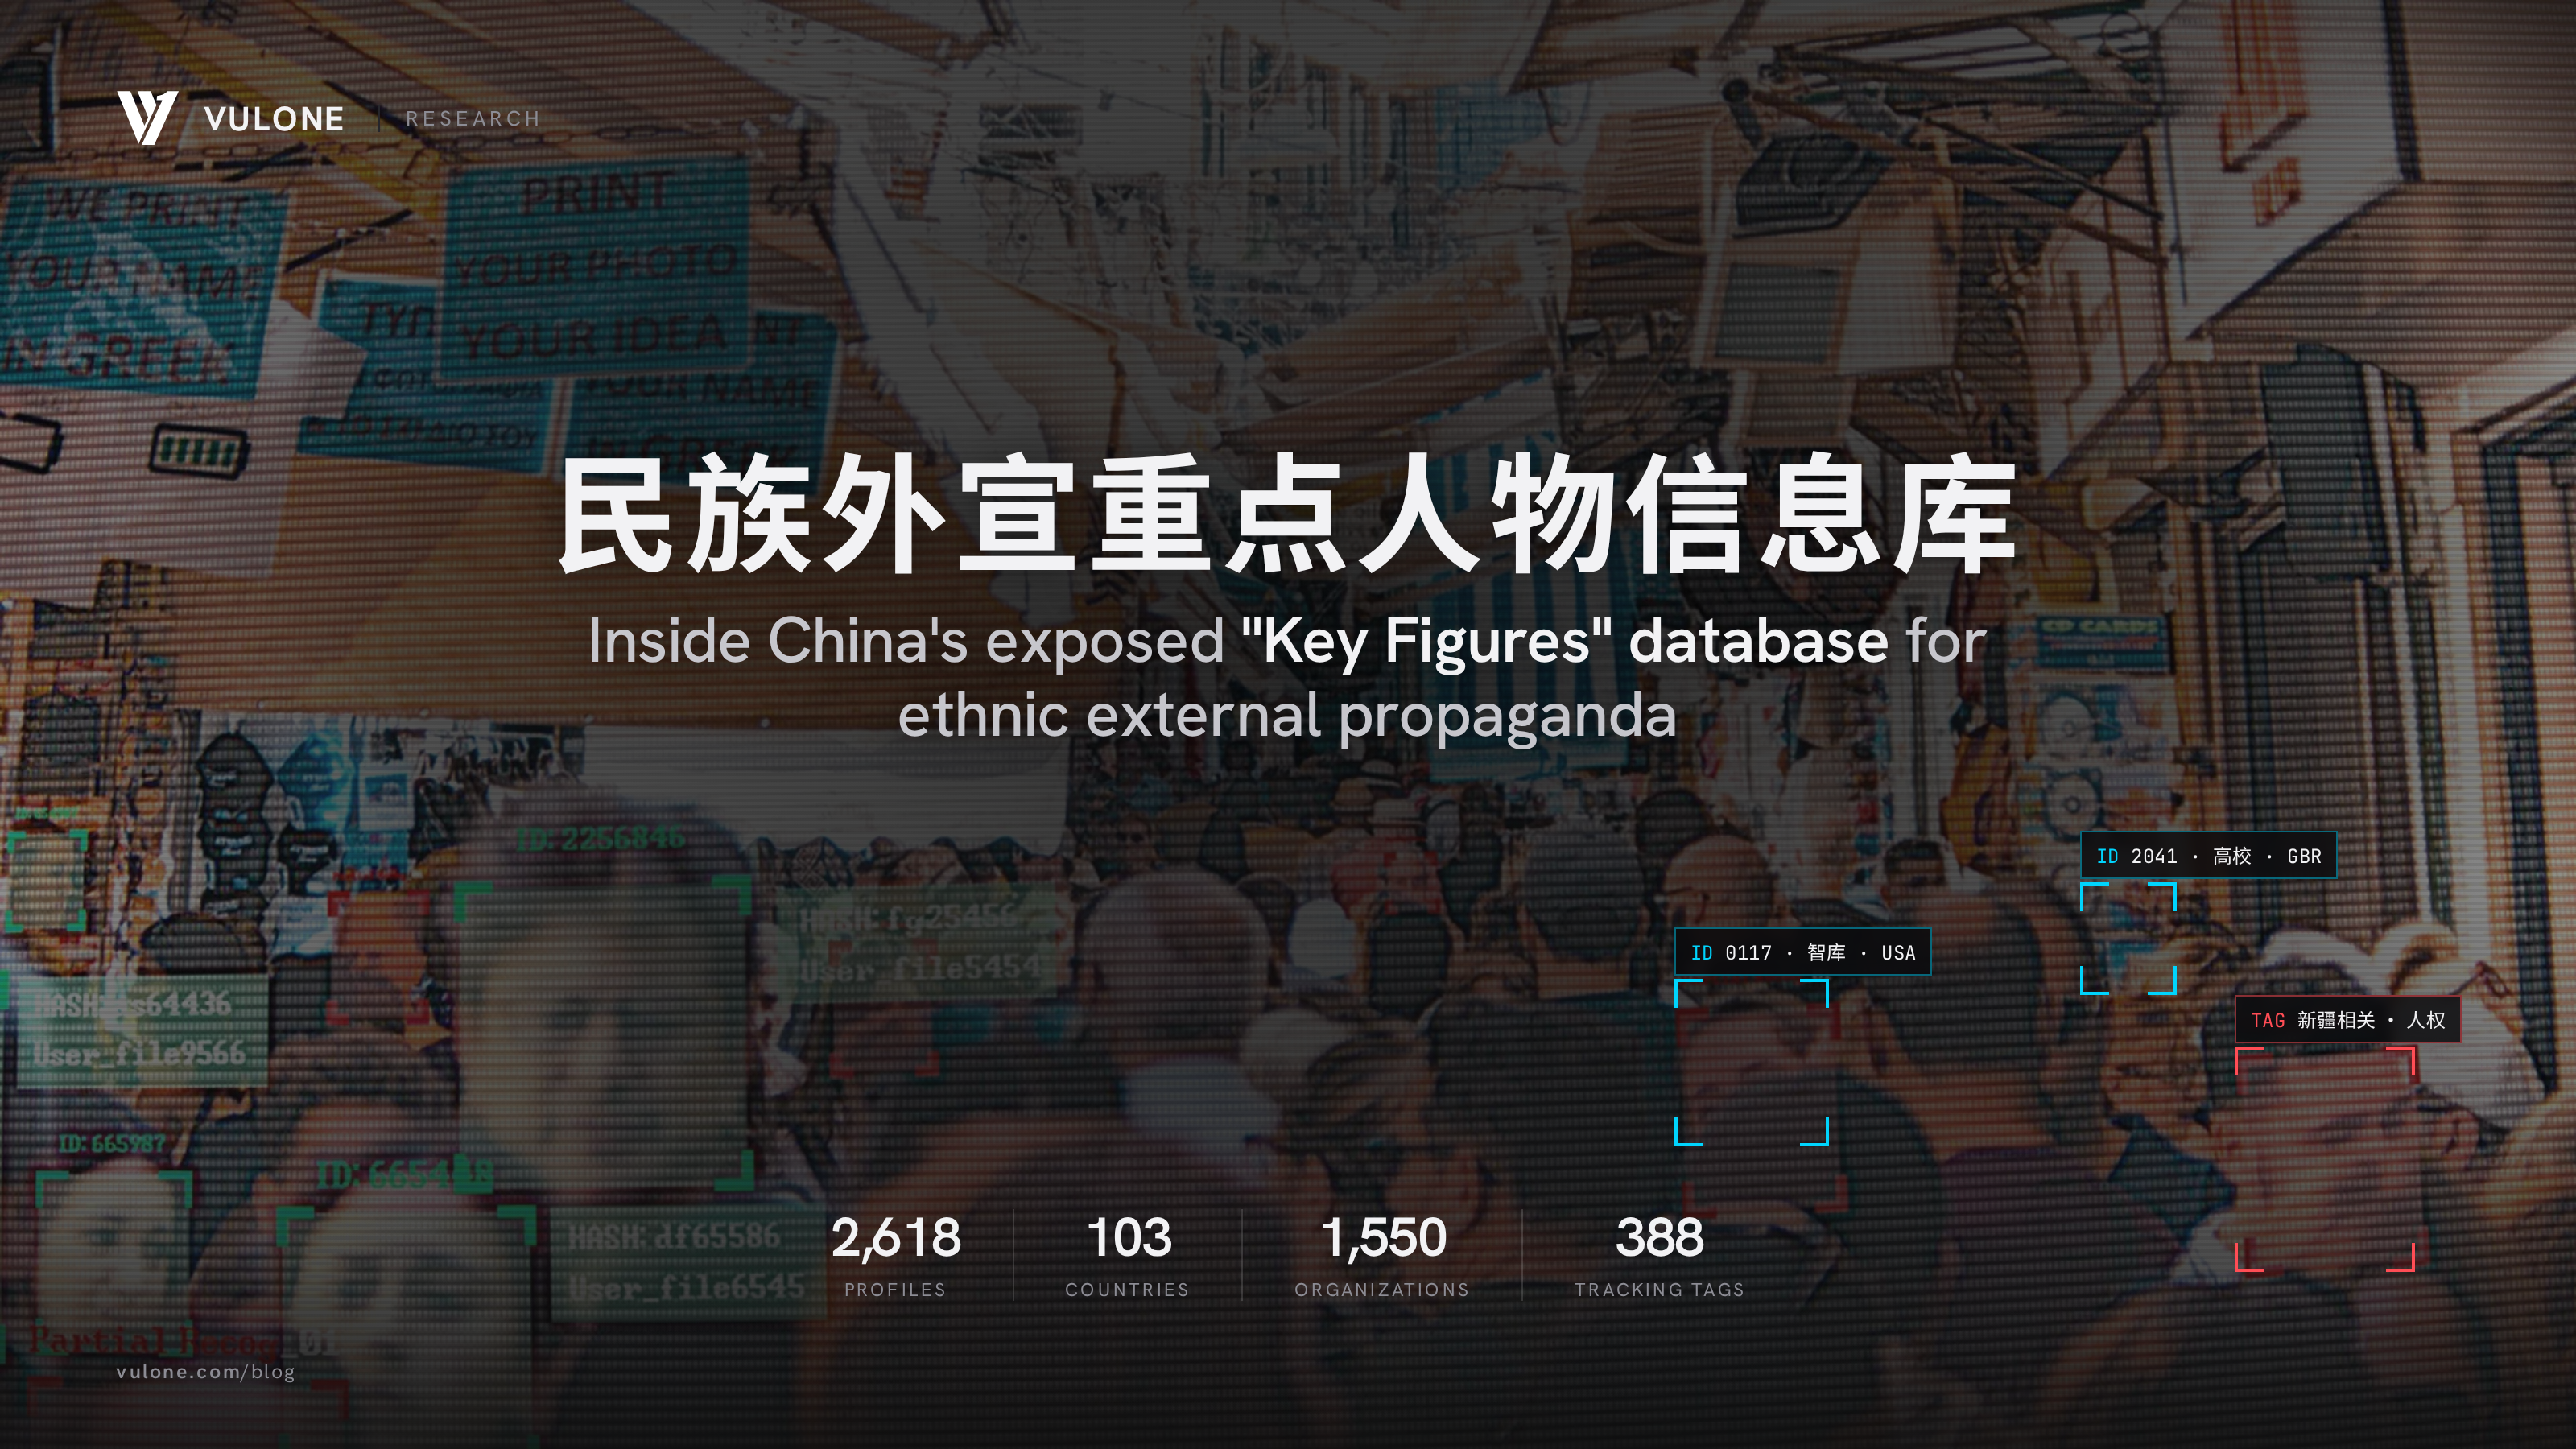
On October 24, 2026, the VULONE Team discovered an operational Chinese database titled 民族外宣重点人物信息库 (Key Figures Information Database for Ethnic External Propaganda). Linked to the China Internet Information Center (CIIC) and DeepChina, it held 2,580 records across 103 countries, structured as a 22-column CRM for tracking and countering voices on ethnic issues. The platform was left unencrypted on the public internet.
Threat Intelligence
Oct 26, 2026
APT Activity
Oct 19, 2026
Threat Intelligence
Sep 15, 2026
VULONE sits in the forums, markets and channels where access and data change hands. The flagship boards, the splinter rooms that outlast every takedown, the Telegram and Discord fronts beside them. When a crew rebrands, rotates or reopens, we are already inside.
See the coverageStart here
Paste a handle, an email, a Tox ID or an address. We return the accounts behind it, the boards they work, and the people they answer to.


